

Entra Policy Suite documentation · Verified against Entra Policy Suite 2.1.4 on Nov 11, 2026
Move from v1
Entra Policy Suite 1 is a set of PowerShell scripts with CSV rule files. Entra Policy Suite 2 runs the same rule engine as a service with a database and a web app. Your v1 rules move across as they are, so the tags your dynamic groups and Conditional Access policies read stay the same.
v1 is never changed by the move. It keeps running until you switch it off, so you can compare both before you do.
What moves
| v1 file | Becomes |
|---|---|
Identity_Tagging.csv and Identity_Tagging_AccountInfo.csv |
User rules, in v1’s order. Rows with the same ConditionGroup become one rule with its conditions joined by AND. |
Device_Tagging.csv |
Device rules |
| The attribute per tag type in v1’s user tagging script | The tag types and their extension attributes |
Entra_Policy_Suite_custom.config |
Settings (group targeting method, authentication strength names, the denied-countries location name), the break-glass accounts and the administrative units |
Entra_Policy_Suite_locked.config |
The target groups the Conditional Access templates use |
EntraNamedLocations_AzureNetworkServiceTags.csv |
The service tag list |
Every value a rule sets becomes an allowed value of its tag type. v1’s demo files are never read.
Two ways to import
Both are in the web app. Nobody needs a database right to import.
Import v1 (everything)
A SuperAdmin opens Overview > Import v1 and chooses the files from v1’s DATA folder - Identity_Tagging.csv, Identity_Tagging_AccountInfo.csv, Device_Tagging.csv, Device_Tagging_AccountInfo.csv, EntraNamedLocations_AzureNetworkServiceTags.csv, Entra_Policy_Suite_custom.config, Entra_Policy_Suite_locked.config - and, for the extension attribute per tag type, v1’s Entra-Policy-Suite\Entra-ID-User-Tagging.ps1. Any part of them is fine.
Read the files shows the plan and saves nothing: area by area (tag types, tag values, user rules, device rules, settings, break-glass accounts, administrative units, target groups, service tags) what is new, what changes (old and new value) and what is already so, with the hints on the rules. Import asks for an optional reason; Entra Policy Suite then writes it within 5 minutes, in one transaction, and the change journal and the audit trail record who imported what.
A second import replaces the rules of the first one and leaves rules you made in the web app alone. The imported rules carry the source “v1-import”, so they can be removed as a set.
To see the same plan on the machine that has the v1 folder, without the web app, Import-EpsV1Data.ps1 reads the folder and shows it; it writes nothing (with -Apply it lists the files to upload):
./Import-EpsV1Data.ps1 -Path <your v1 folder>
Only the rules
On the Tagging Rules page, choose the Grid view and Import CSV …. Upload Identity_Tagging.csv (or Device_Tagging.csv). The page shows the plan before anything is staged: the rules it would create, the hints on them, and any value your install does not have yet. Tick add the missing values to add those values to their tag types in the same change, before the rules that set them - otherwise add them on the Tag types page first. The import is staged in the Commit queue like any other change, and an admin commits it.
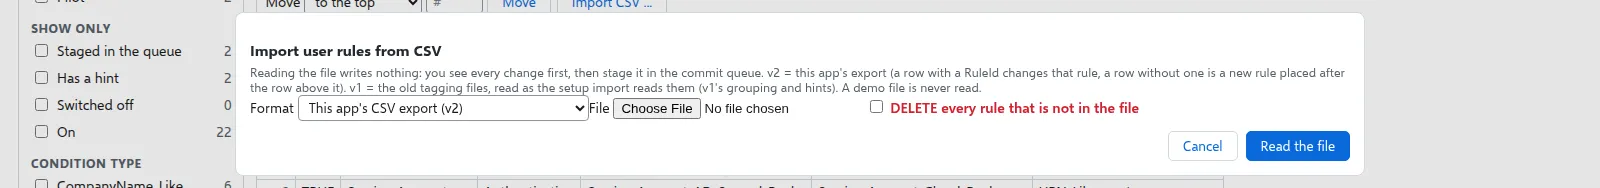
The same dialog imports and exports the rules in the Entra Policy Suite 2 CSV format, so you can keep a copy or edit many rules in Excel.
Hints the import shows
The import marks rows that are probably a mistake, without stopping:
- a rule that can never match (two conditions that contradict each other);
- a rule that never wins, because an earlier rule for the same tag type always matches first;
- the same condition twice in one rule;
- an unknown condition type (for example a typo);
- rows that share a ConditionGroup with different targets on the same field - typically rows that were copied and kept the original’s group, which joins them to the original rule by AND;
- a value mode that does not fit its tag type.
Fix them on the Tagging Rules page after the import, or in the CSV before it.
Switch over
- Import, then run user and device tagging in Preview on everyone. With the same rules, the plan should show few or no changes: v1 already wrote the same tags.
- Run an Apply on a test scope and check the users in the Tag changes page.
- Switch v1’s scheduled tasks off, then set the tagging mode to Apply.
Two v1 issues that Entra Policy Suite 2 does not have: the rule order is an explicit number (it does not depend on the PowerShell version), and the identity report reads Active Directory once per run through the hybrid worker.
Verified against Entra Policy Suite 2.1.4 on 2026-11-11
Verified against Entra Policy Suite 2.1.4 on Nov 11, 2026