

A portal whose identity only reads your directory
The portal's identity has read-only directory permissions; changes are queued and carried out by the engine. Each visit requires Entra sign-in.
Purpose
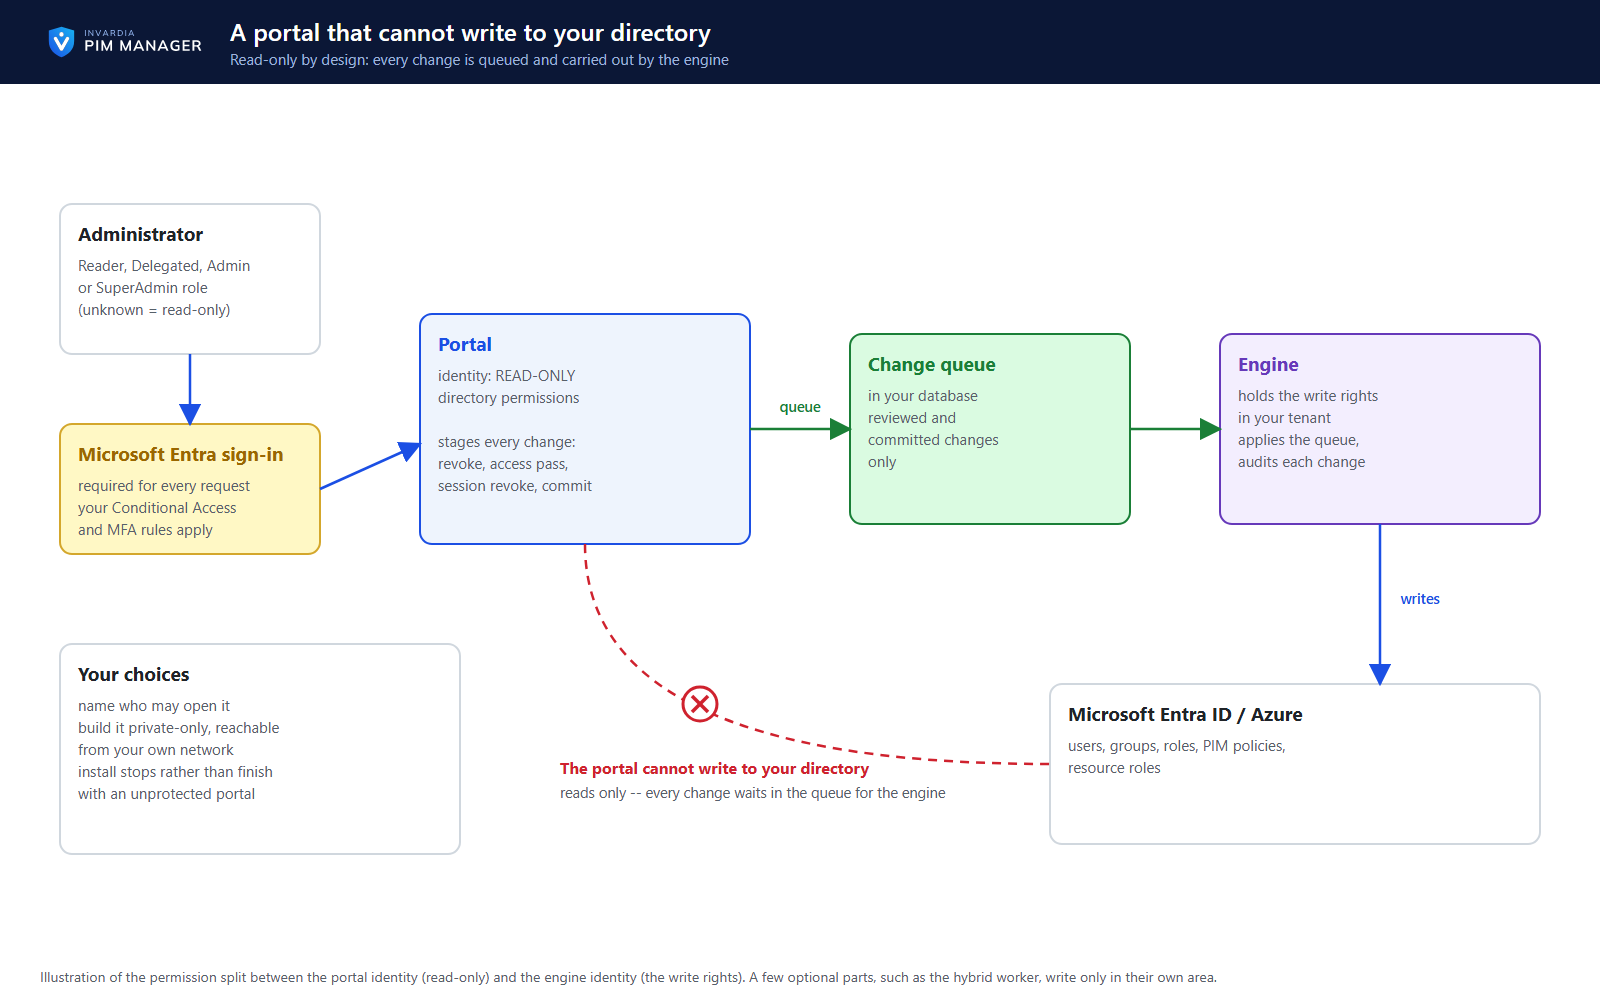
A web console with write access to Entra is a prime target. A stolen PIM Manager session cannot write to Entra ID directly: what it can stage and commit is limited by that user's Manager role and by the guards, and the engine applies it.
Design
The portal holds read-only directory permissions. A revoke, an access-pass re-issue, a session revoke or a commit is queued and applied by the engine, the component whose identity writes to your directory. Each visit passes Microsoft Entra sign-in, and the installation stops rather than finish with an unprotected portal. You can name who may open it, and a private-only deployment, reachable from your own network, is supported.
Inside, each user is a Reader, Delegated, Admin or SuperAdmin; if a role cannot be determined, the user gets read-only access.
Business opportunities
Layered protection for the tool that manages your most privileged access - and a straightforward story for your security review.
Related features
An engine that keeps your tenant matching your model
You describe the access you want; the engine creates the groups, owners, policies, assignments and access passes your data defines, and keeps them that way.
One queue for the changes you make - reviewed, backed up, reversible
Configuration edits, revokes, access-pass re-issues and session revokes wait in one queue until someone commits them.
Drift: live versus desired, with a decision for each difference
See what is missing, what was changed and what is extra in the tenant - and decide what happens to each item: Apply now, Import into PIM, Delete, Ignore or Re-add.
PIM policy changes wait for a SuperAdmin
A policy run plans its changes and holds them until a SuperAdmin approves that exact change set, with the setting that weakens protection marked.