

MSP: central admin accounts, removed across tenants at once
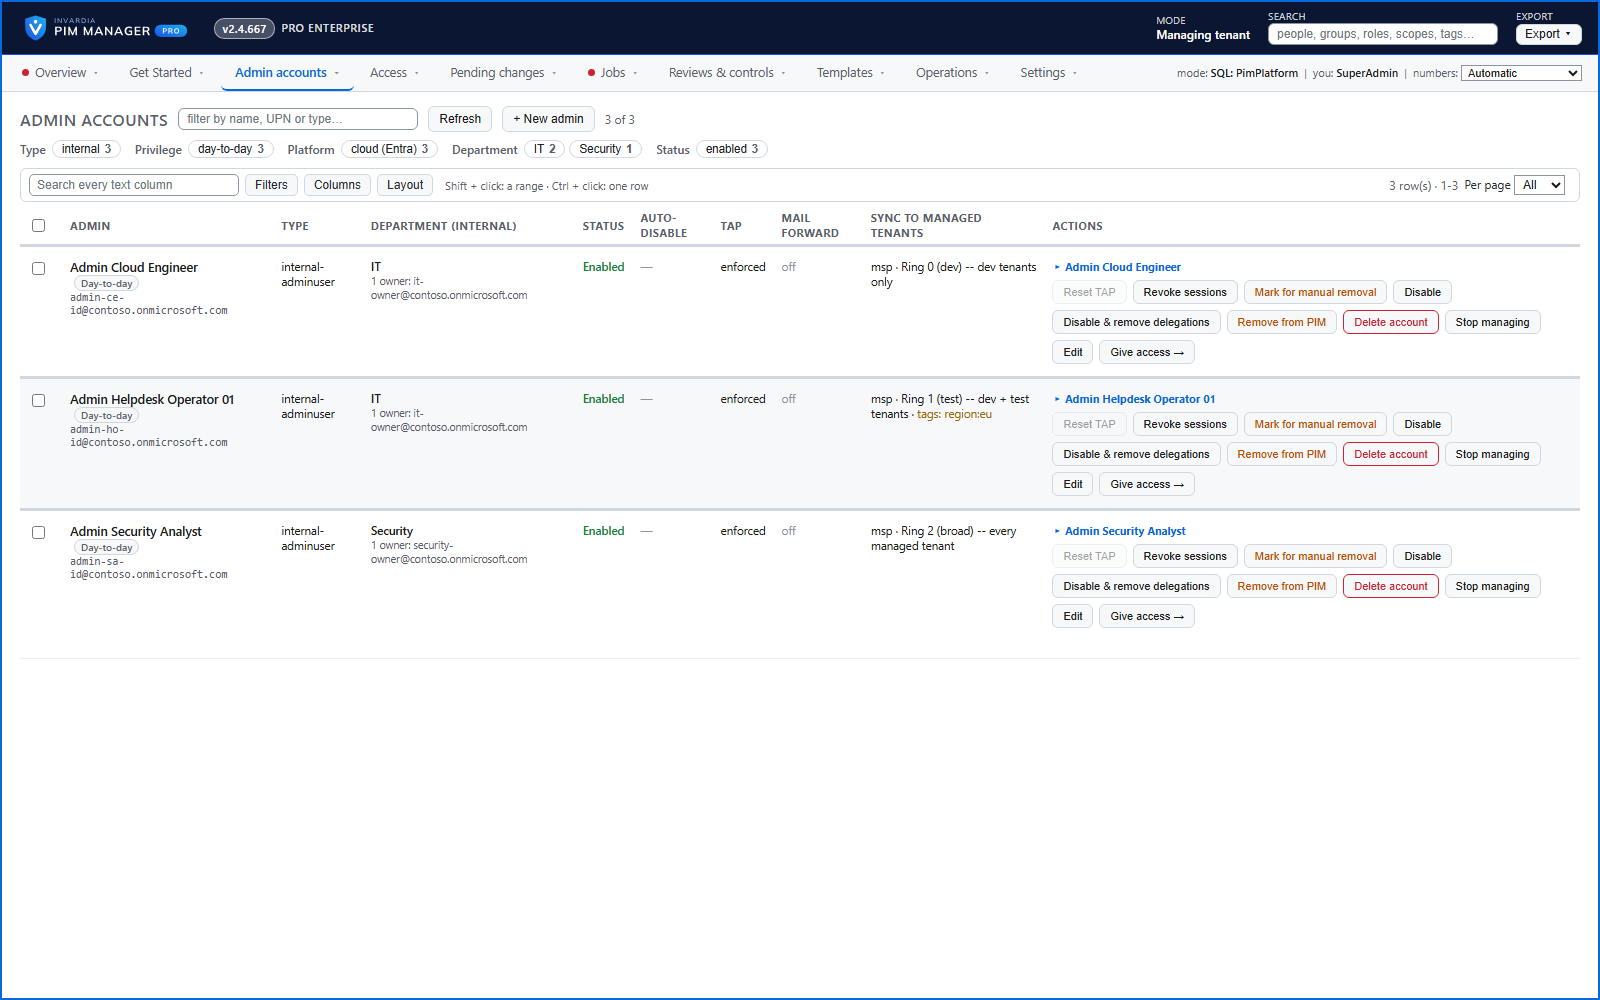
Provider admins flow down to the tenants that need them, with status and auto-disable date - and a leaver's access ends in the managed tenants on their next sync.
Purpose
When a provider's engineer leaves, their access must end in each customer tenant the same day.
Design
An admin is synced to managed tenants only when its record says so, optionally narrowed by tags, or where a replicated delegation names that person. Status and auto-disable date flow down with it. Revoking an admin's sessions on the managing tenant can revoke them in the managed tenants on their next sync, and a signed instruction can disable or revoke an account across tenants - applied locally by each tenant's own engine. Removing an admin asks whether all, some or none of the managed tenants should remove it too. On a managed tenant each record shows whether it came from the provider or is local.
Business opportunities
Provider access is governed centrally and ends across tenants at once, while each customer keeps control of its own local admins.
Related features
Access map: your delegation model on one board
Pick a person or a permission and see every path in your delegation model - people, their groups, what those groups include and the roles and scopes they grant.
Look up a role: find the least-privileged role for the job
See what an Entra ID role can do in plain words, find the roles that grant an action ranked least-privileged first, see who can activate a role, or compare two roles.
PIM Activator: activate the access you need, together
A browser extension for Edge and Chrome: tick the groups and roles you need, give one justification and activate them together - three clicks for a typical activation.
PIM policy changes wait for a SuperAdmin
A policy run plans its changes and holds them until a SuperAdmin approves that exact change set, with the setting that weakens protection marked.