

Delegated administration of the Manager
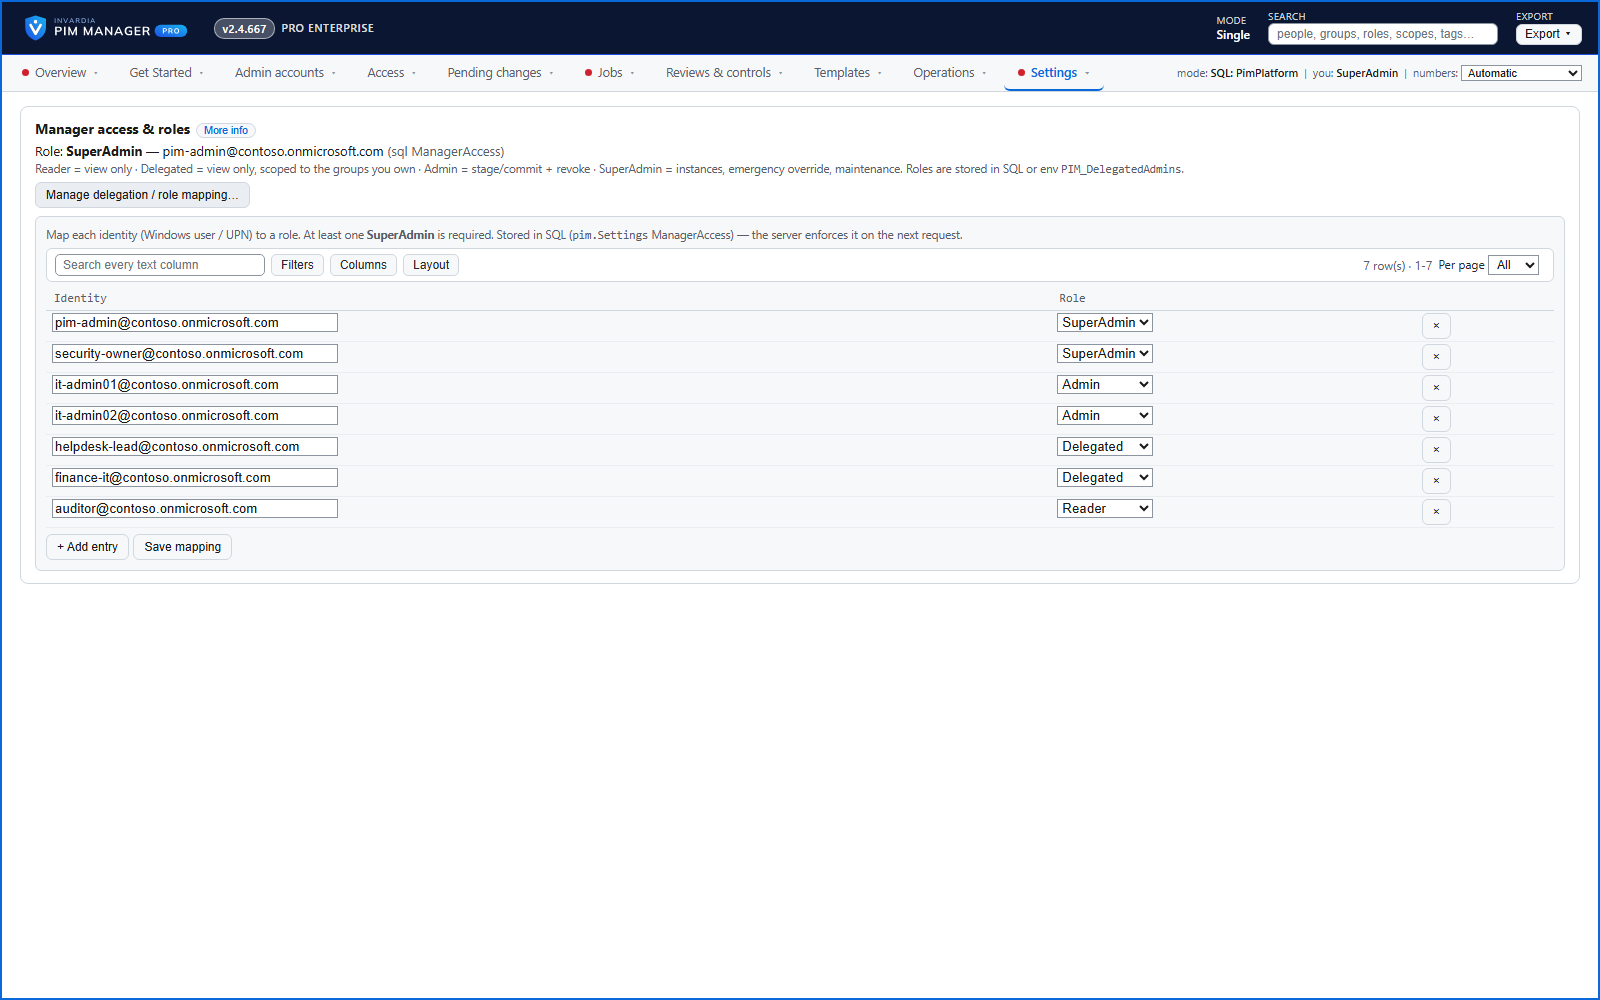
Each identity is a Reader, Delegated, Admin or SuperAdmin in the Manager; a Delegated user, limited by tier, level, service or scope, sees and changes only what they own.
Purpose
Workload owners should manage their own delegations without seeing - or touching - the most privileged tiers.
Design
Settings > Manager access & roles maps each identity to Reader, Delegated, Admin or SuperAdmin. A delegated profile carries the services, the tier and level ceilings, the scopes and the admins its holder may manage. A Delegated user sees only the groups they own, the admin list hides the tiers above their ceiling, and anything outside the scope is refused and audited. SuperAdmins are not limited by a profile.
Business opportunities
Spread the day-to-day work to the teams who own each workload while central IT keeps control of Tier 0.
Related features
Access map: your delegation model on one board
Pick a person or a permission and see every path in your delegation model - people, their groups, what those groups include and the roles and scopes they grant.
Look up a role: find the least-privileged role for the job
See what an Entra ID role can do in plain words, find the roles that grant an action ranked least-privileged first, see who can activate a role, or compare two roles.
PIM Activator: activate the access you need, together
A browser extension for Edge and Chrome: tick the groups and roles you need, give one justification and activate them together - three clicks for a typical activation.
PIM policy changes wait for a SuperAdmin
A policy run plans its changes and holds them until a SuperAdmin approves that exact change set, with the setting that weakens protection marked.