

One audit trail, with before and after
Commits, approvals, setting changes, refusals and guard trips by the Manager and the engine in one append-only trail - who, what, when, the result, and the value before and after.
Purpose
"Who granted this access, and when?" should have one answer, not a search across portal logs, scripts and mailboxes.
Design
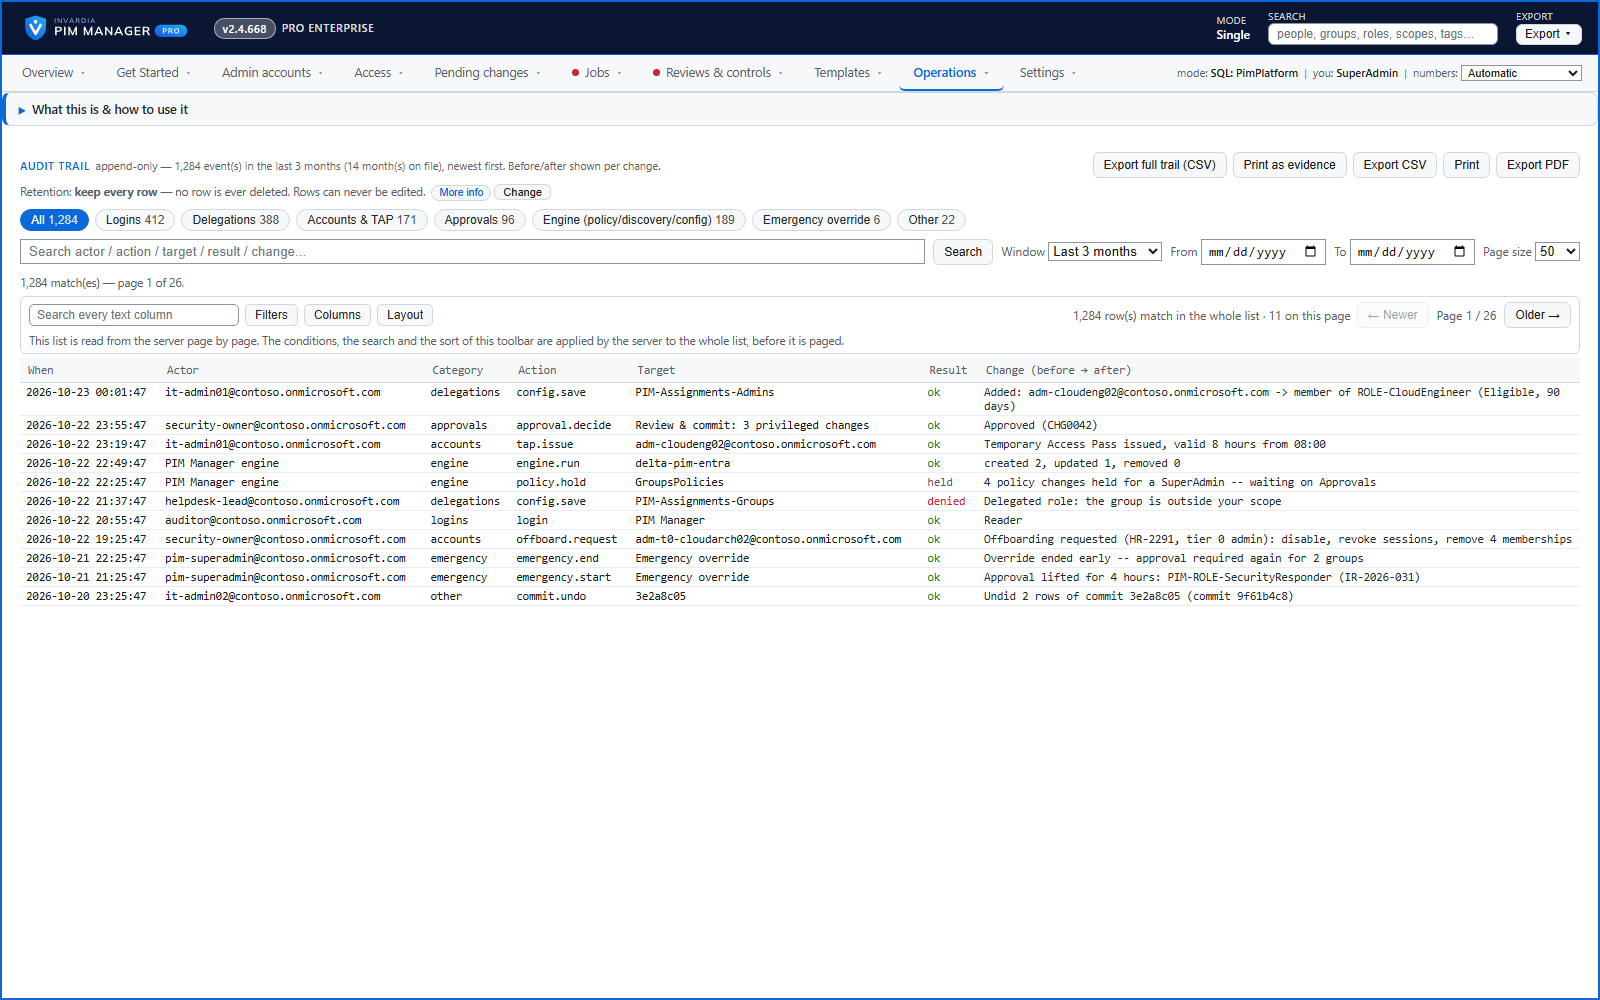
The Manager and the engine write to the same append-only audit trail in your database: commits, approvals, setting changes, refusals and guard trips, with the before and after values. The engine records the memberships, role assignments and account changes it makes or fails to make, with the real names, and policy changes rule by rule. Commits read as one sentence per changed row.
The Audit trail page filters by category, searches and chooses a time window. Exporting the full trail and printing it as evidence are available in Pro editions; the export is spreadsheet-ready and protected against formula injection.
Business opportunities
Audit questions are answered from one place, with evidence you can hand over as it is.
Related features
Who can do what - and who can activate this role
Pick a person to see the targets they can reach, or pick a role to see who can activate it - each with the exact path that grants it.
One queue for the changes you make - reviewed, backed up, reversible
Configuration edits, revokes, access-pass re-issues and session revokes wait in one queue until someone commits them.
A second administrator for sensitive changes
Maker and checker: with the Pro second approver on, the most sensitive changes need a different administrator's approval before they are carried out. It is off by default.
Delegation overview: the active privileged assignments right now
The active Entra ID role, Azure role and PIM for Groups assignments in your tenant in one view, opening at once from a stored snapshot.