

Stale identity clean-up
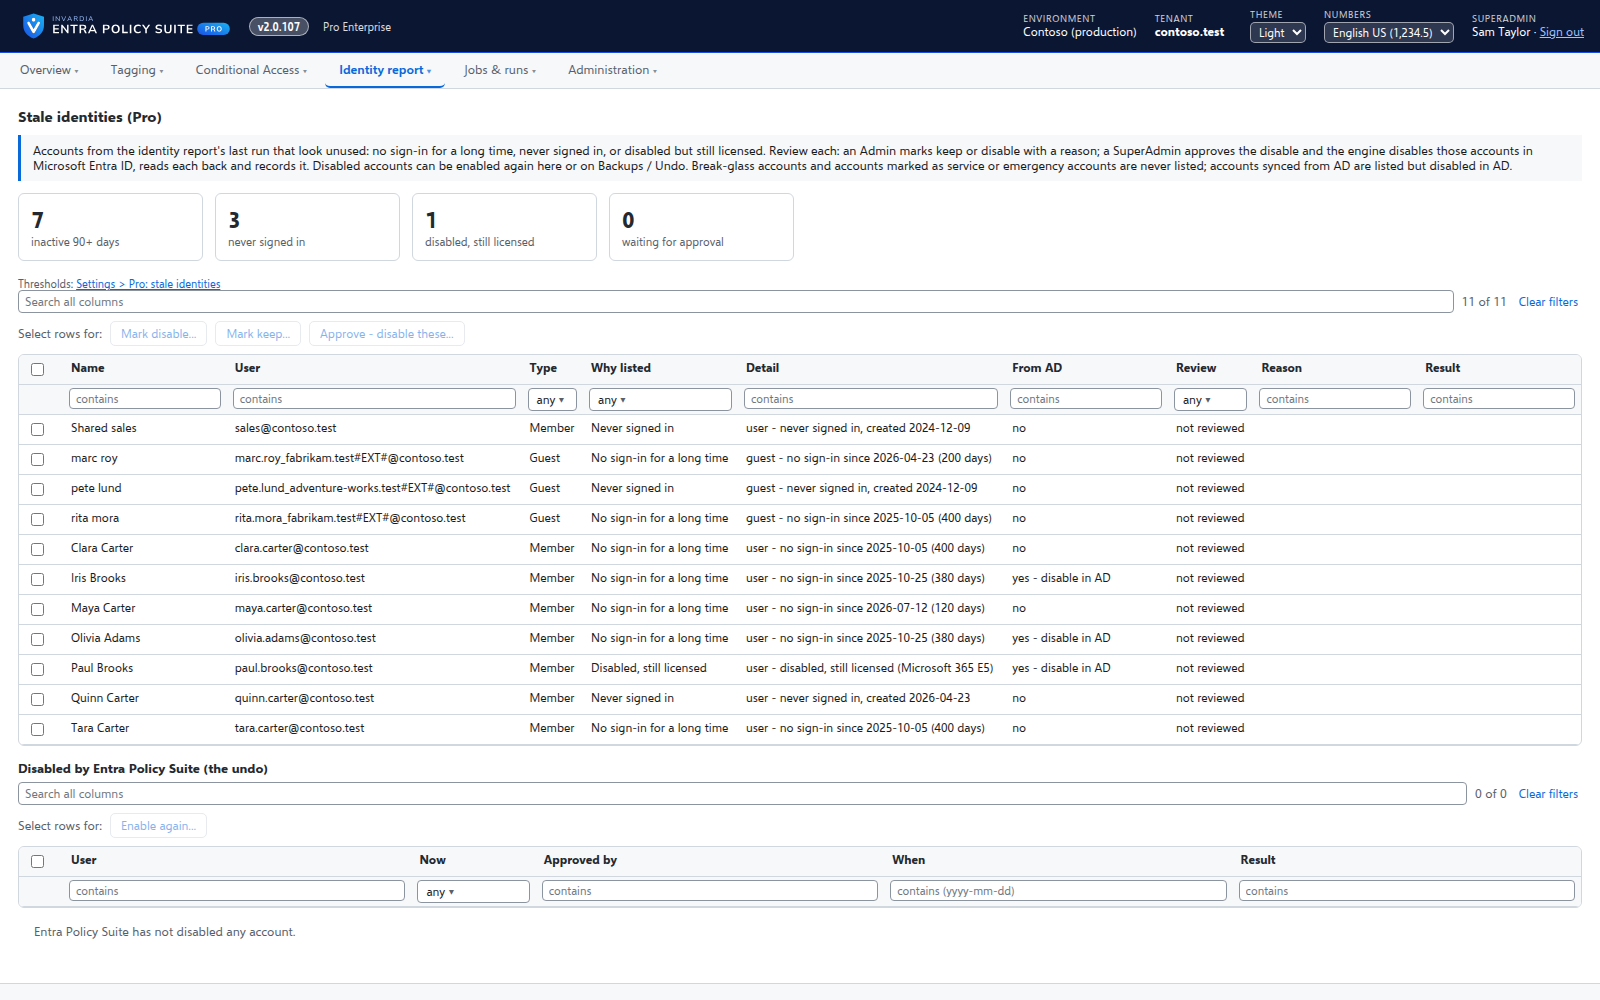
Pro: users and guests with no sign-in for 90 days, never signed in, or disabled but still licensed - reviewed, approved and only then disabled.
Purpose
Inactive accounts are a way into the tenant and often still cost a license. Disabling them in bulk without a review breaks the accounts someone still needs.
Design
The list comes from the identity report (the 90 days is a setting). An Admin marks each account keep or disable with a reason, a SuperAdmin approves, and only then are the approved accounts disabled - each read back, recorded and audited, and enabled again from the same page. Break-glass and service accounts are never listed; accounts synced from AD are disabled in AD.
Business opportunities
Fewer accounts an attacker can use and fewer licenses on people who left, with a reviewer and a record for every account.
Related features
Rules you edit like a spreadsheet
Every tagging rule on one page, edited like Excel: select, copy and paste, fill down, duplicate, move and switch on or off - many rules at once.
A commit queue for every rule change
A saved change waits until an admin commits it - nothing reaches the directory the moment someone types.
The identity report as gap views
A daily, read-only snapshot of every user and device, shown as gaps with a severity and how to close them.
Changes applied by the engine, every one audited
A change made in the web app is carried out by the engine for the person who made it, and recorded in an append-only audit trail.