

Changes applied by the engine, every one audited
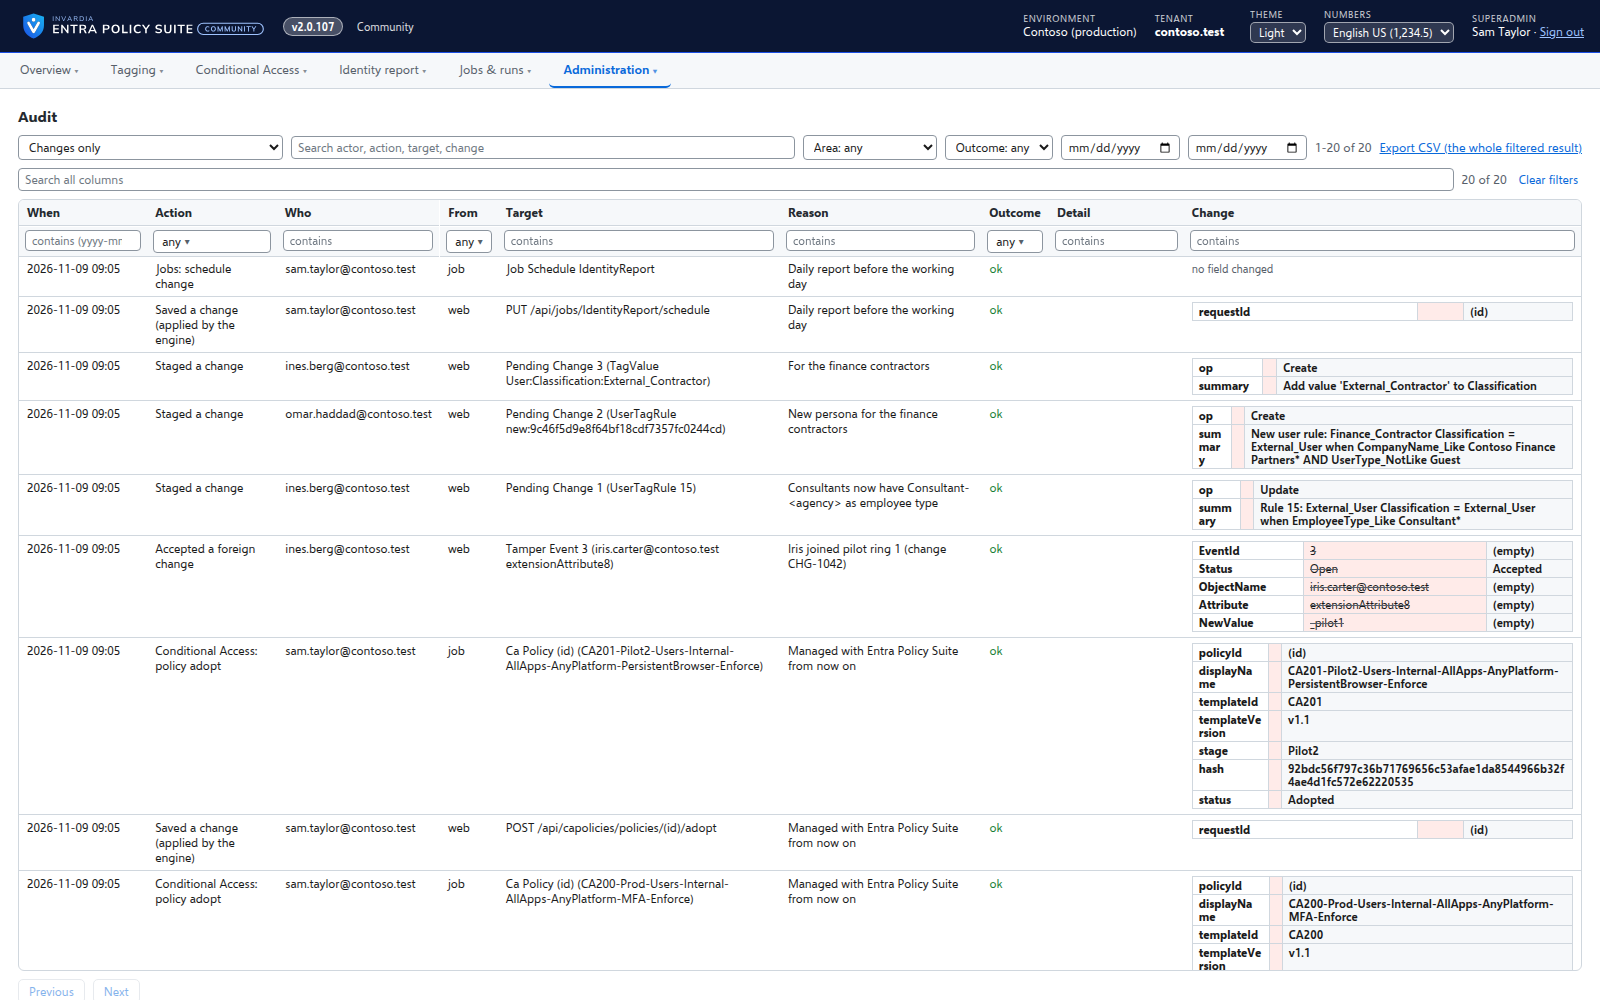
A change made in the web app is carried out by the engine for the person who made it, and recorded in an append-only audit trail.
Purpose
A web app that can write to your directory is a target. Changes must come from a named person with the right role, and leave a record that cannot be edited afterwards.
Design
The web app records each change with the signed-in person and their reason; the engine applies it, usually within a few minutes, after it checks the person's role at that moment, and the page shows when it is applied. The web app's own identity cannot change the directory or the configuration. Every change and every refused request is in the audit trail with who, when, why, before and after; the database refuses to change or delete an audit row.
Business opportunities
Auditors get a complete, tamper-proof record of who changed what and why, and the web app is not a way into your directory.
Related features
Rules you edit like a spreadsheet
Every tagging rule on one page, edited like Excel: select, copy and paste, fill down, duplicate, move and switch on or off - many rules at once.
A commit queue for every rule change
A saved change waits until an admin commits it - nothing reaches the directory the moment someone types.
Bring your Entra Policy Suite 1 rules
The v1 rule files import as they are, so the tags your groups and policies read stay the same.
Conditional Access you move stage by stage
Adopt the Conditional Access policies you already have, move each one to Pilot or Prod with a button, and see when a policy drifts or loses its break-glass exclusion.