

Conditional Access policy as code
Pro: your managed Conditional Access policies as JSON files - as a zip, or pushed to GitHub or Azure DevOps - reviewed in a pull request and read back.
Purpose
Teams that review infrastructure as code want the same review for Conditional Access: a diff, a pull request and a history in Git.
Design
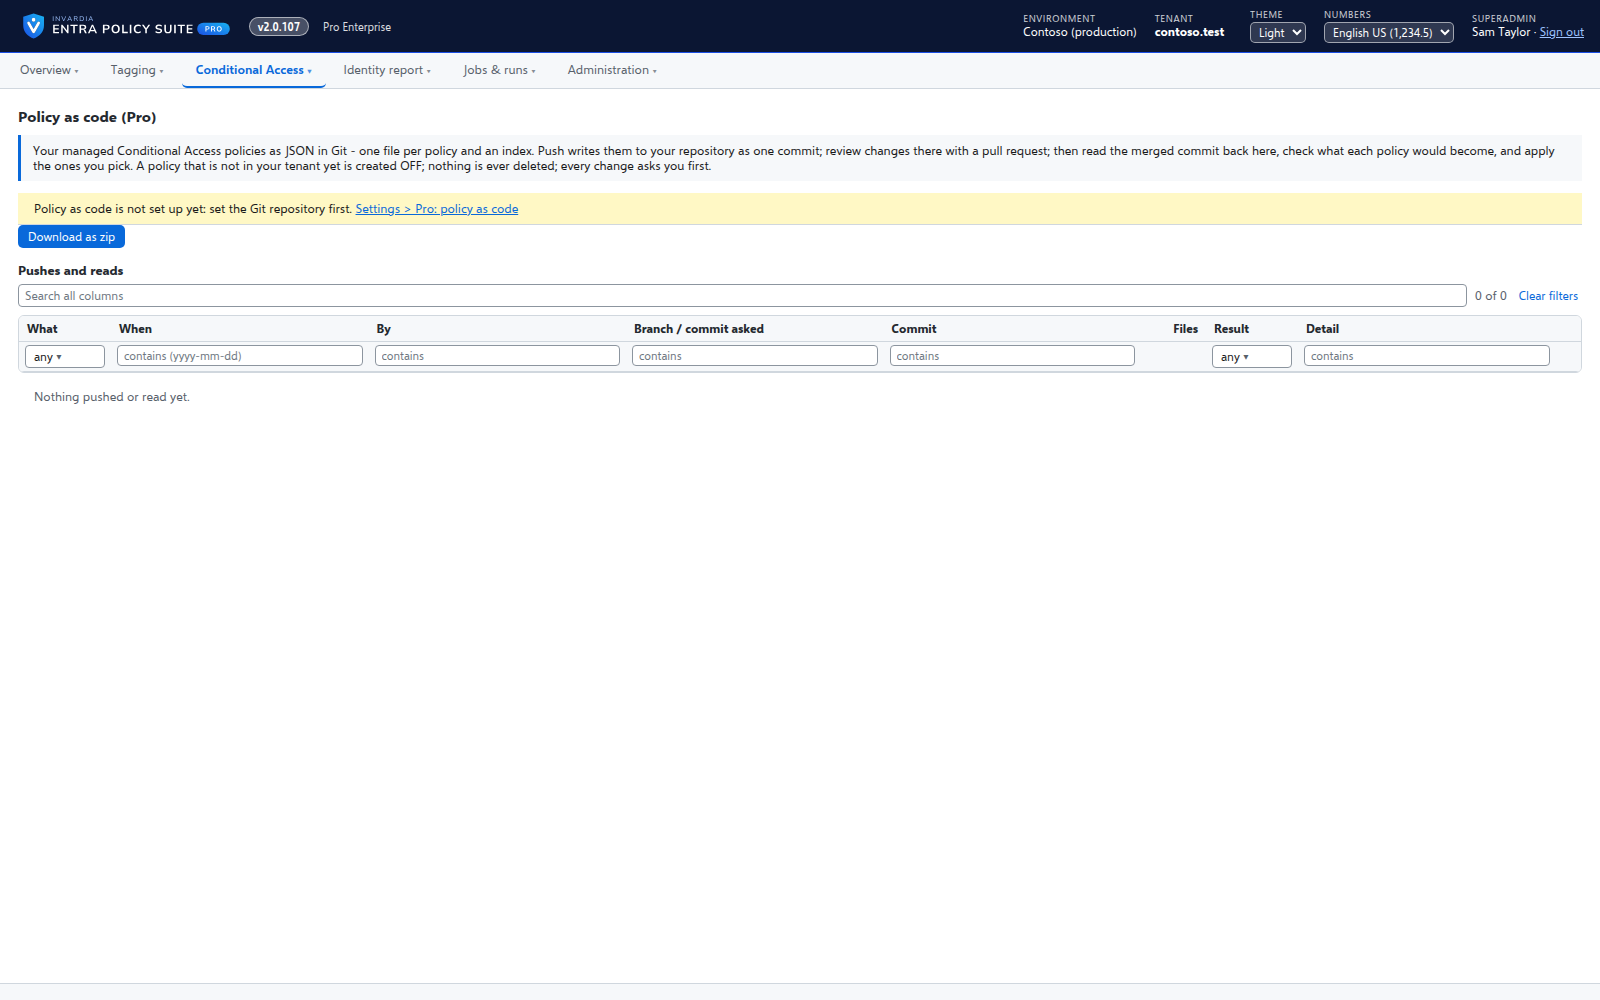
Export the managed policies as JSON - one file per policy and an index - as a zip, or push them to your GitHub or Azure DevOps repository as one commit. Review there with a pull request, then read the merged commit back: per policy new, changed or the same, and the policies Git does not have. You pick what to apply, and it goes through the same restore as the Backups page (the plan, the break-glass check, a backup first, a new policy created off, never a delete). The Git access key stays in your own Key Vault; push and read need a Key Vault right that your Key Vault administrator grants.
Business opportunities
Conditional Access gets the same pull-request review and Git history as the rest of your infrastructure.
Related features
Rules you edit like a spreadsheet
Every tagging rule on one page, edited like Excel: select, copy and paste, fill down, duplicate, move and switch on or off - many rules at once.
A commit queue for every rule change
A saved change waits until an admin commits it - nothing reaches the directory the moment someone types.
Changes applied by the engine, every one audited
A change made in the web app is carried out by the engine for the person who made it, and recorded in an append-only audit trail.
Bring your Entra Policy Suite 1 rules
The v1 rule files import as they are, so the tags your groups and policies read stay the same.