

One asset, every source: cross-source correlation
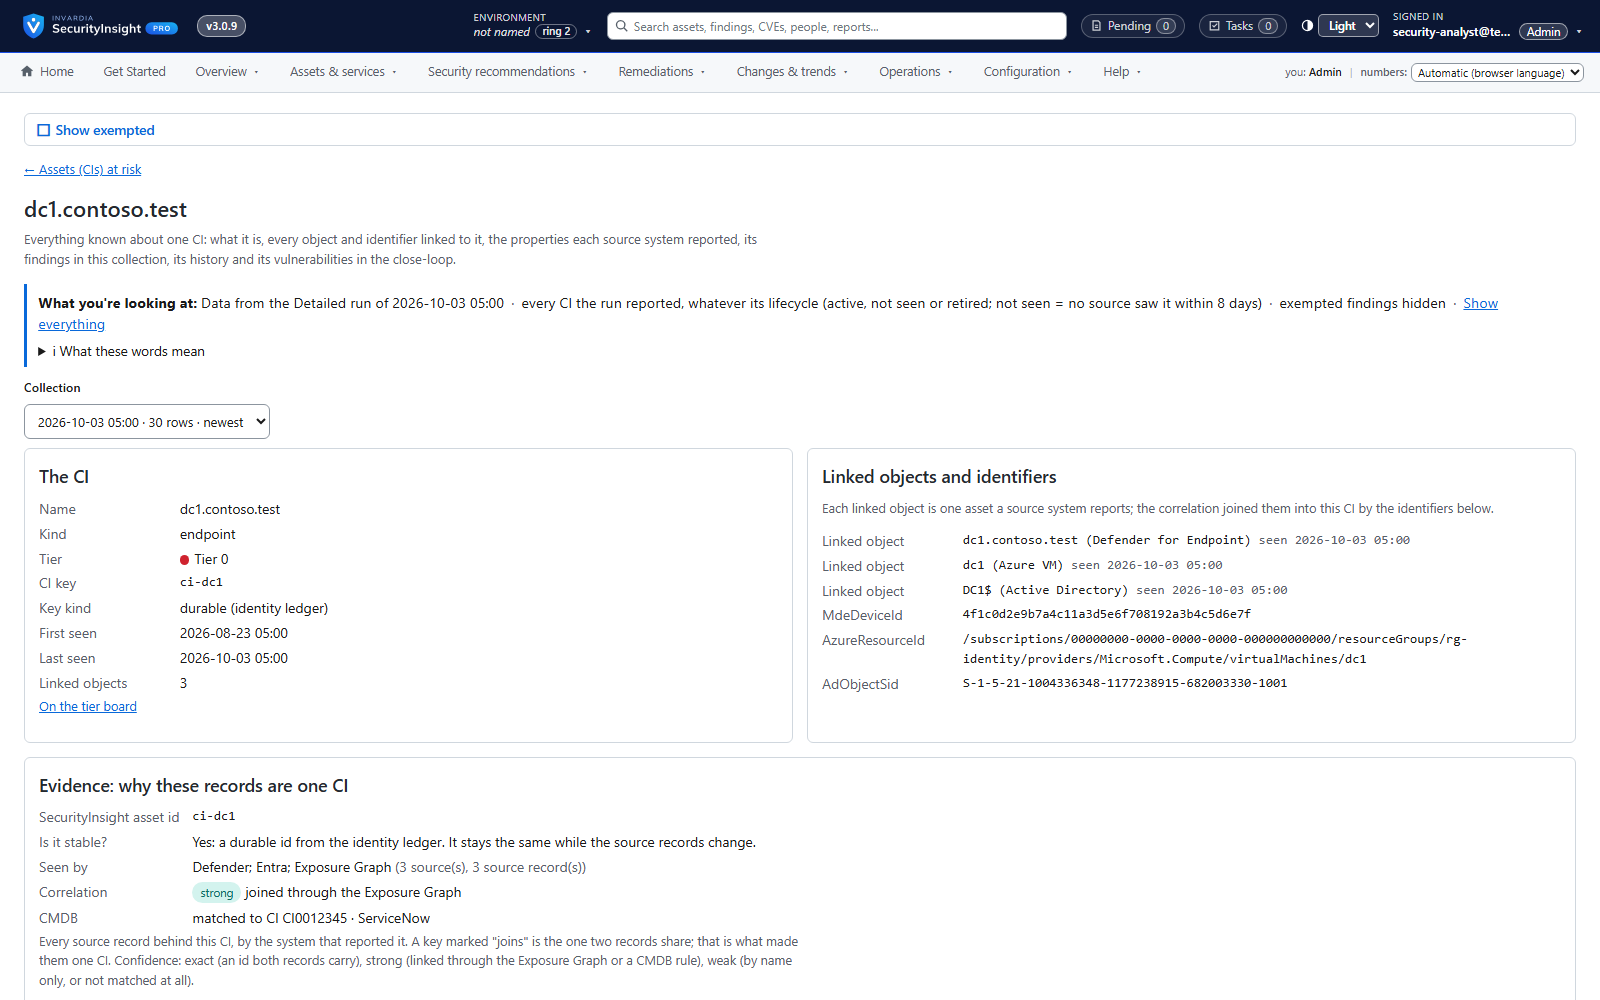
A server seen by Defender, as an Azure VM and in Active Directory becomes one CI with one history.
Purpose
The same machine shows up under different names and ids in every tool, so findings are counted twice, owners are unclear and nobody sees the whole story of one asset.
Design
A correlation stage joins the objects every source reports into one configuration item with a stable id, keeps every identifier beside it, and records which source reported what. The CI view shows everything known about one asset: its identifiers, what each source says, its history across collections, its vulnerabilities in the close-loop and its findings.
Business opportunities
Fewer duplicate tickets, clean hand-over to the CMDB, and one place to answer "what do we know about this server?" in seconds.
Related features
Asset profiling across endpoints, identities, Azure and public IPs
One profile per asset - device, identity, Azure resource or public IP - built automatically from the data you already have.
Privilege tier catalog
Every role and permission in your tenant ranked by what an attacker could do with it - Tier 0 to Tier 3.
Tier board with explained decisions
See every asset in its tier and exactly which signal put it there - and move it with one drag.
Fifteen views of every collection
Raw rows, correlated CIs, vulnerabilities, risk, MITRE, compliance, CVSS, exemptions, lifecycle, what changed, connector changes and services - for any collection.