

Fifteen views of every collection
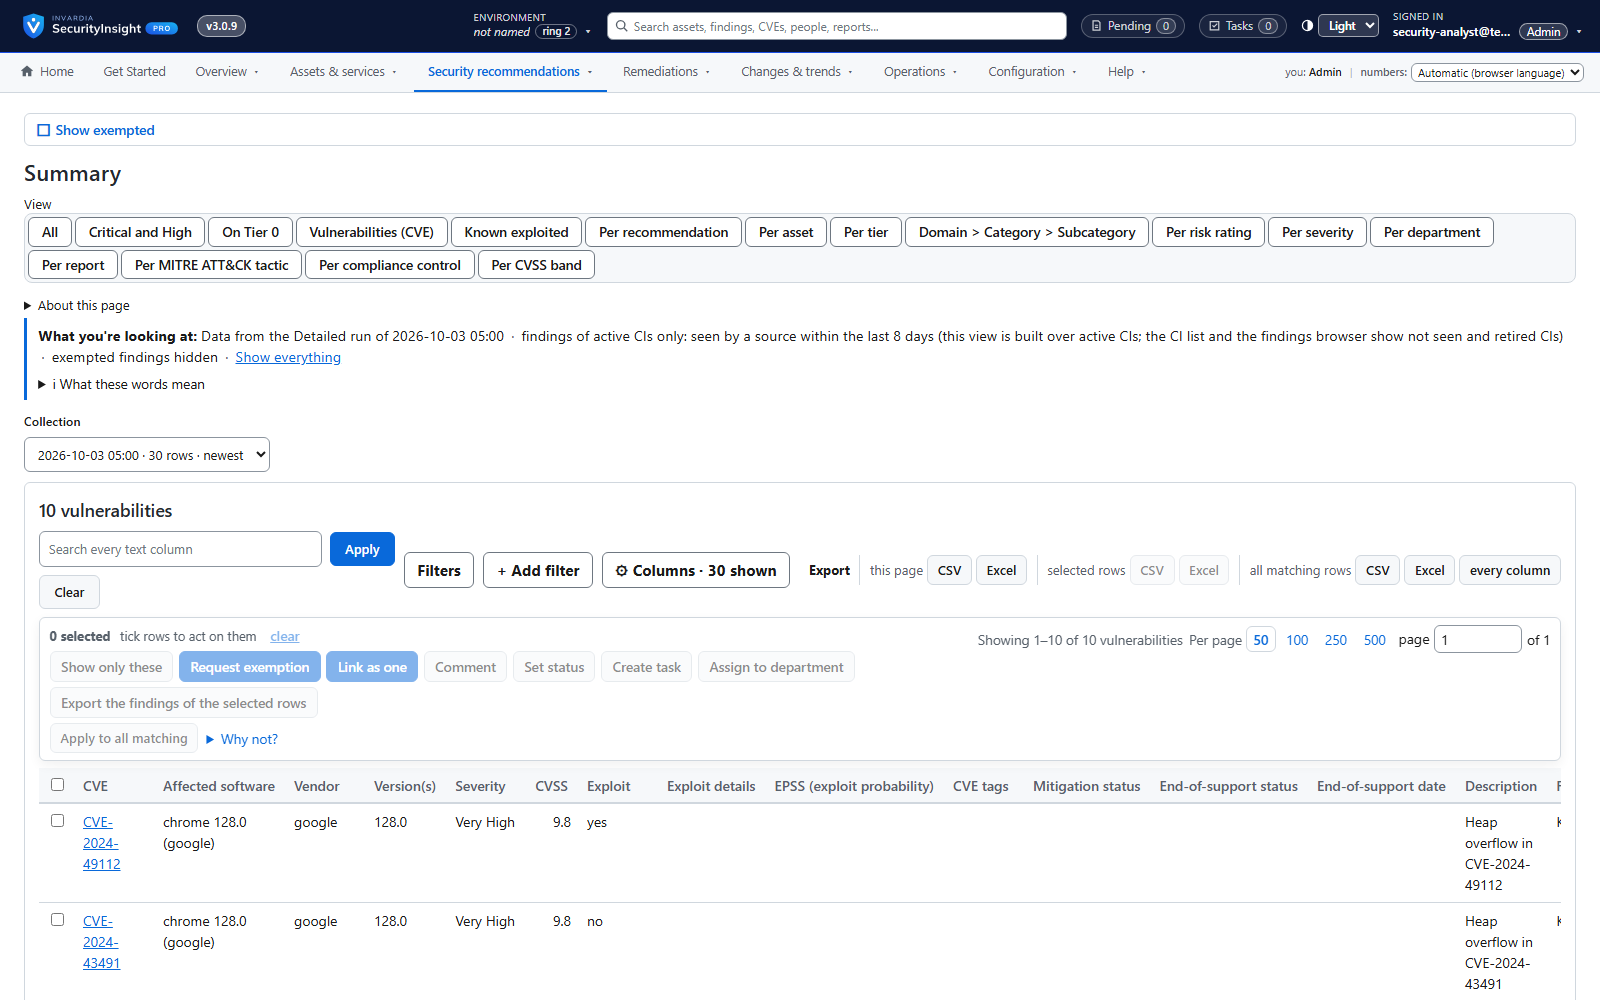
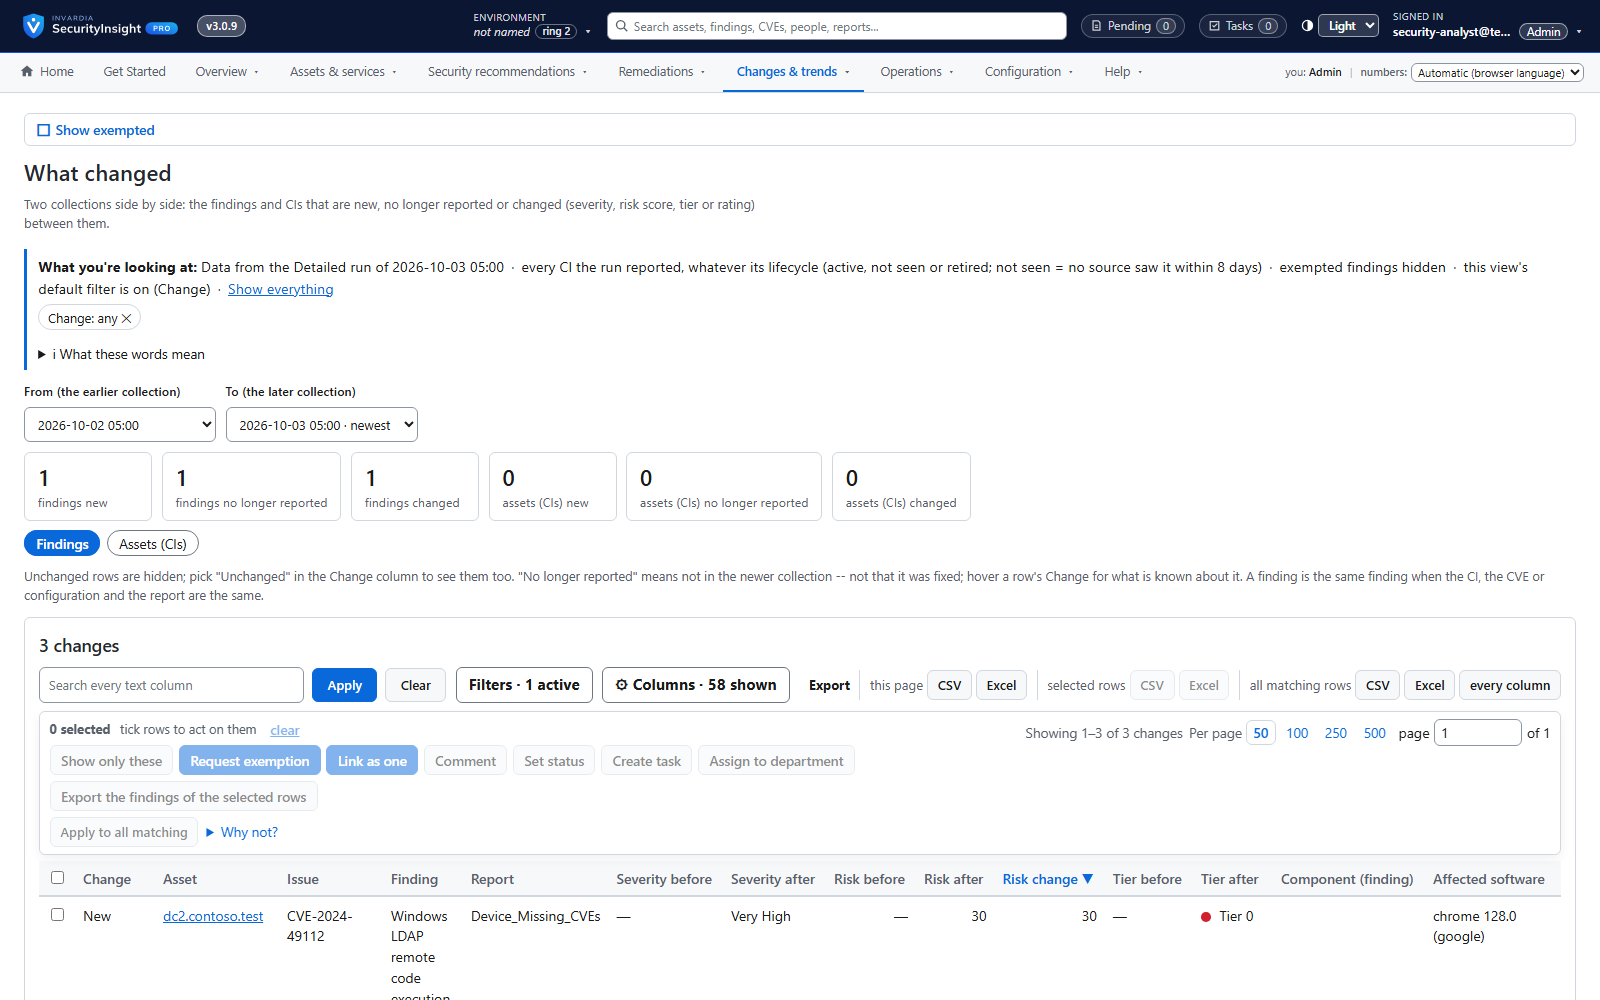
Raw rows, correlated CIs, vulnerabilities, risk, MITRE, compliance, CVSS, exemptions, lifecycle, what changed, connector changes and services - for any collection.
Purpose
Different people ask different questions of the same data: the engineer wants the CVE, the manager wants the change since last week, the auditor wants the exemptions in force.
Design
Each collection opens in fifteen views that share one fast grid: sort on any column, filter several values at once, search, select rows, page on the server and export the whole filtered view to Excel or CSV. The state lives in the address, so a link opens exactly the same view. Views read pre-computed data from the Pro database, never Log Analytics per page view.
Business opportunities
Self-service answers for every role without building reports, and fast enough to use in a meeting.
Related features
Asset profiling across endpoints, identities, Azure and public IPs
One profile per asset - device, identity, Azure resource or public IP - built automatically from the data you already have.
One asset, every source: cross-source correlation
A server seen by Defender, as an Azure VM and in Active Directory becomes one CI with one history.
Privilege tier catalog
Every role and permission in your tenant ranked by what an attacker could do with it - Tier 0 to Tier 3.
Tier board with explained decisions
See every asset in its tier and exactly which signal put it there - and move it with one drag.