

Privilege tier catalog
Every role and permission in your tenant ranked by what an attacker could do with it - Tier 0 to Tier 3.
Purpose
Thousands of Entra roles, Graph permissions and Azure roles exist, and most organisations cannot say which of them hand over the keys to the kingdom.
Design
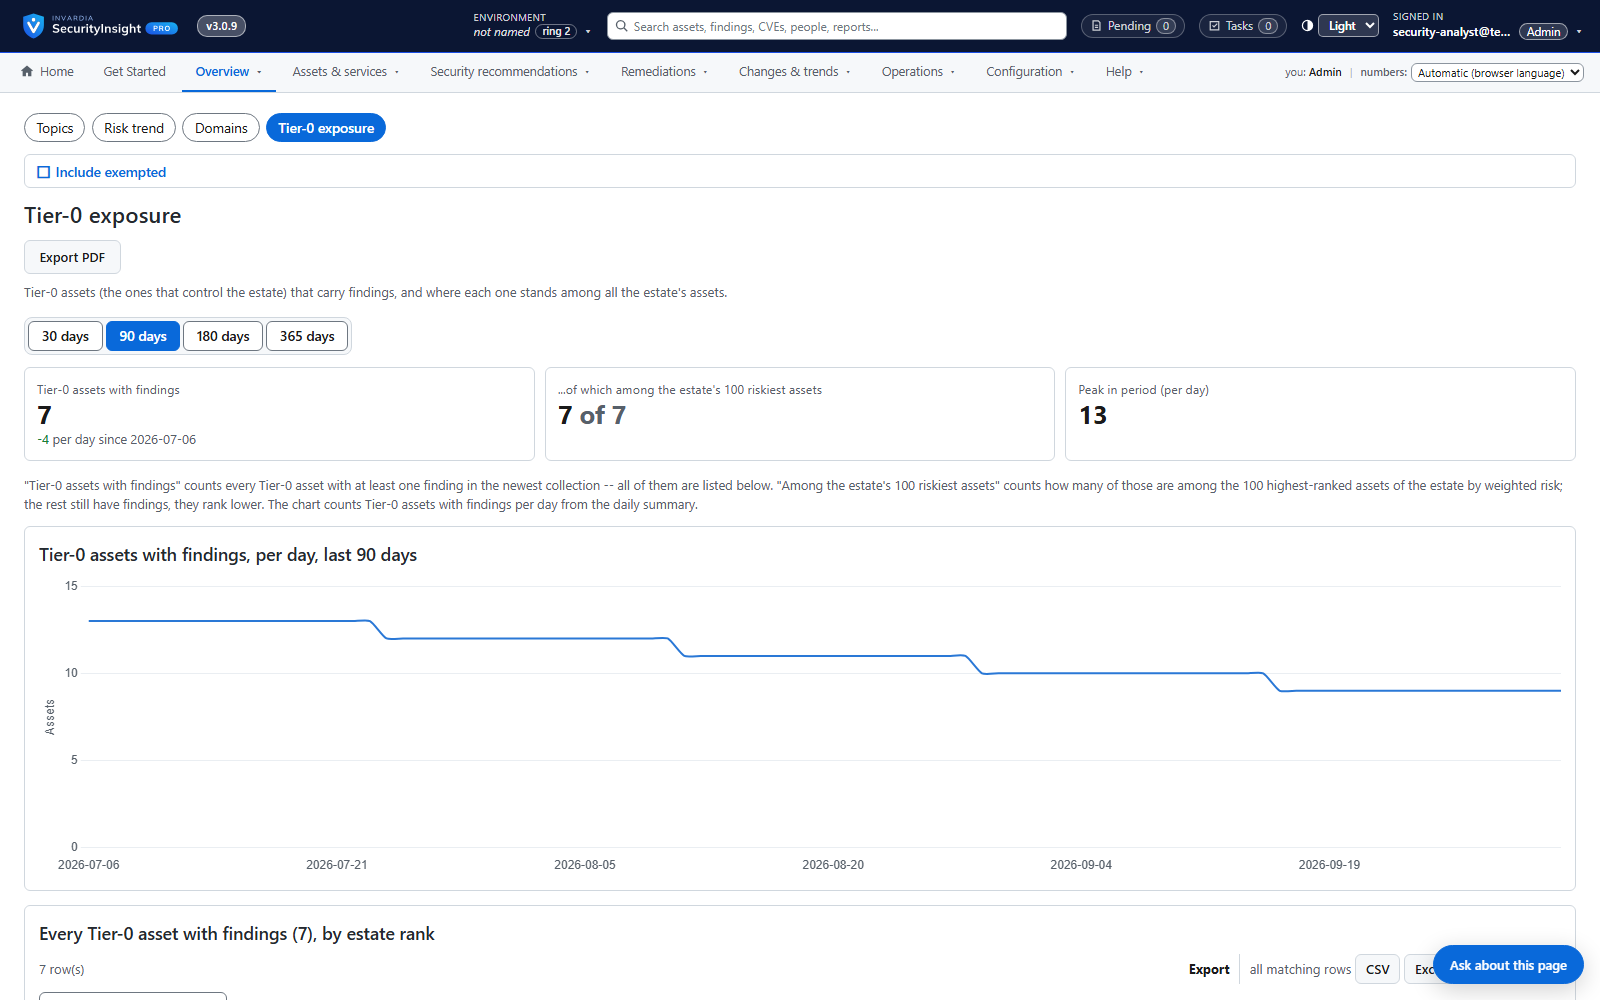
The privilege-tier classifier builds a catalog that places every role and permission on an attacker-centric tier scale, optionally helped by your own Azure OpenAI for roles it has not seen before. The profilers use the catalog to tier every identity, device and resource; you can add your own roles on top. Community ships the catalog and runs the classifier as a script; in Pro, the Tier-0 exposure page lists every Tier-0 asset with findings and where it ranks in the estate.
Business opportunities
Focus protection on the small set of assets that control everything else - the basis of any tiered administration model and a clear story for auditors.
Related features
Asset profiling across endpoints, identities, Azure and public IPs
One profile per asset - device, identity, Azure resource or public IP - built automatically from the data you already have.
One asset, every source: cross-source correlation
A server seen by Defender, as an Azure VM and in Active Directory becomes one CI with one history.
Tier board with explained decisions
See every asset in its tier and exactly which signal put it there - and move it with one drag.
Public IP exposure with Shodan
See your internet-facing addresses the way an attacker does, tied to the asset behind them.