

Asset profiling across endpoints, identities, Azure and public IPs
One profile per asset - device, identity, Azure resource or public IP - built automatically from the data you already have.
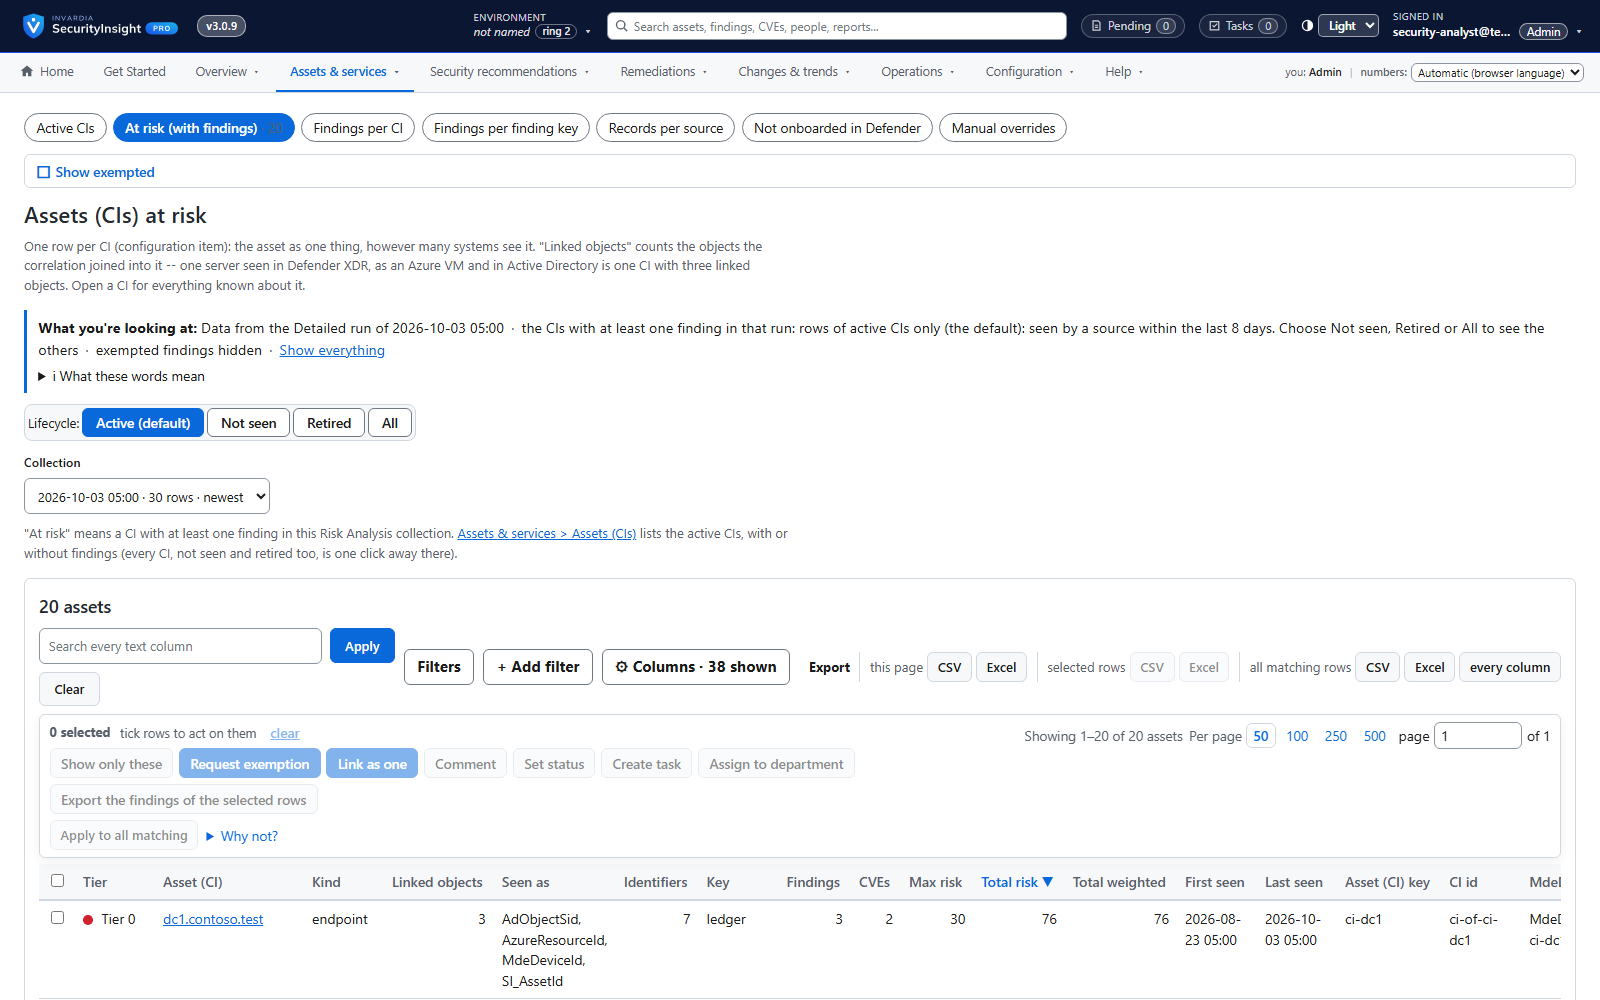
Purpose
Security teams rarely lack data; they lack one trustworthy view of what they own. Devices live in Defender, identities in Entra ID, resources in Azure, and nobody can say with confidence which of them matter most.
Design
Four collection engines read Microsoft Defender XDR, Entra ID, Azure Resource Graph and Log Analytics without installing agents, and write one flat profile per asset to your own Log Analytics workspace. Detection rules recognise what each asset is - a domain controller, a certificate authority, a SQL server, a privileged account - and record the evidence. Collection is read-only.
Business opportunities
A complete, always-current asset inventory with business context, without a discovery project. Security, IT operations and risk owners finally work from the same list.
Related features
One asset, every source: cross-source correlation
A server seen by Defender, as an Azure VM and in Active Directory becomes one CI with one history.
Privilege tier catalog
Every role and permission in your tenant ranked by what an attacker could do with it - Tier 0 to Tier 3.
Tier board with explained decisions
See every asset in its tier and exactly which signal put it there - and move it with one drag.
Public IP exposure with Shodan
See your internet-facing addresses the way an attacker does, tied to the asset behind them.