

A CMDB in SecurityInsight - or your own
Keep your service catalog in SecurityInsight, or connect the CMDB you already have.
Purpose
Many organisations have no CMDB, or one that is out of date, yet need services and owners to prioritise risk.
Design
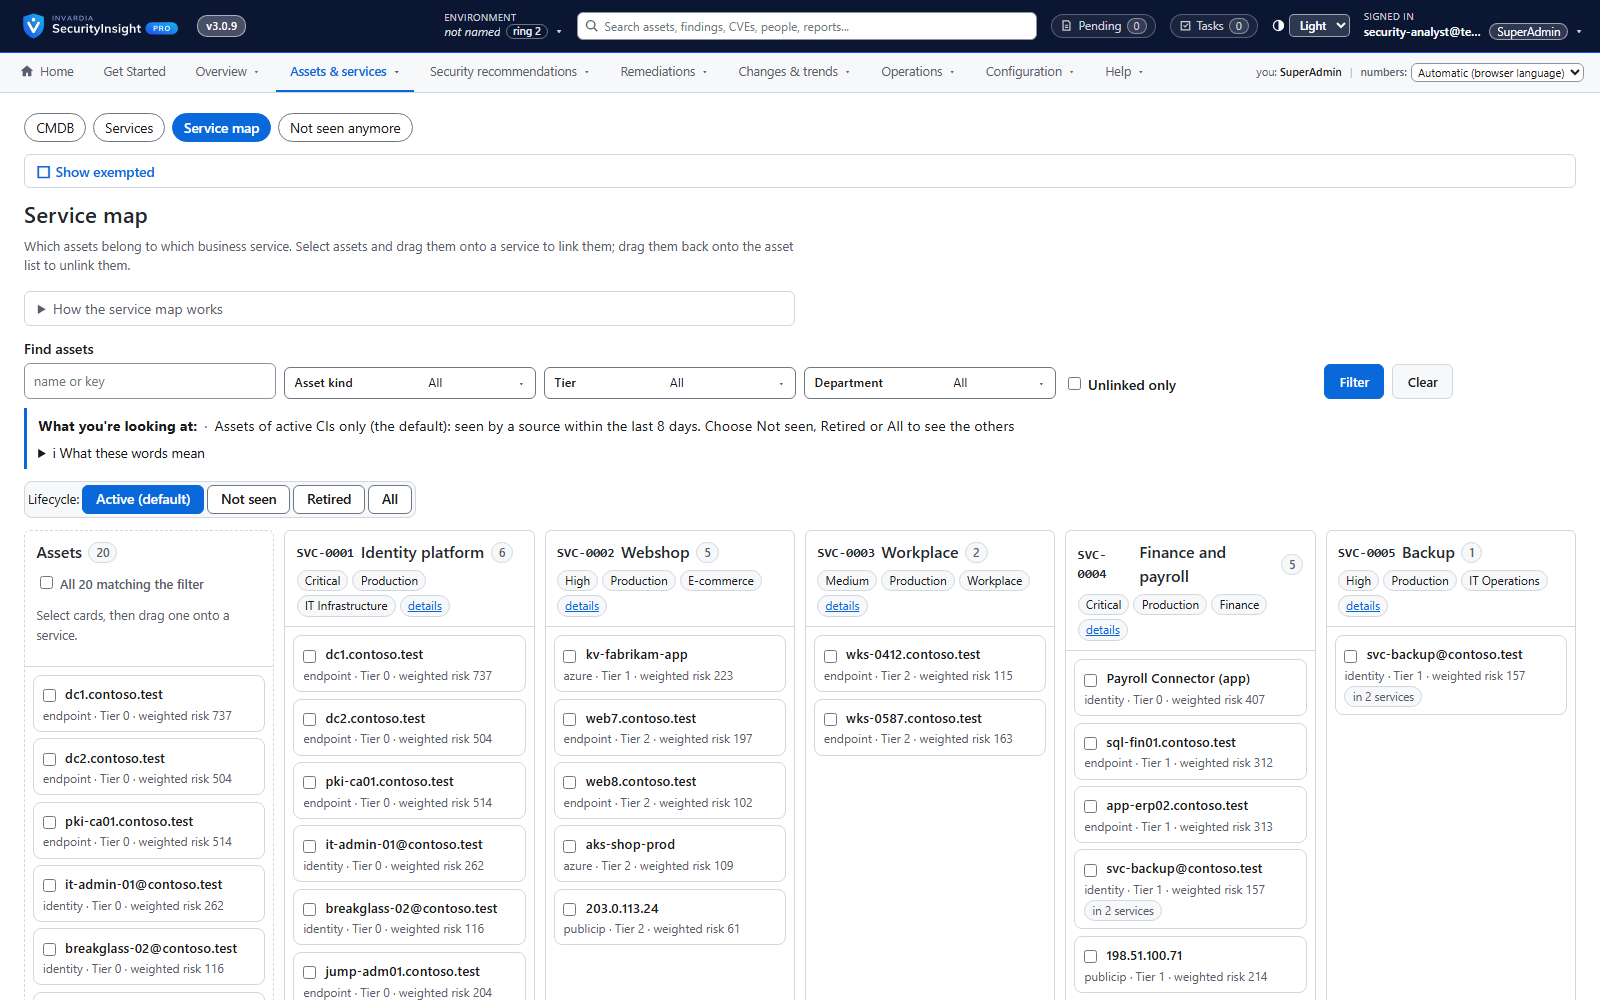
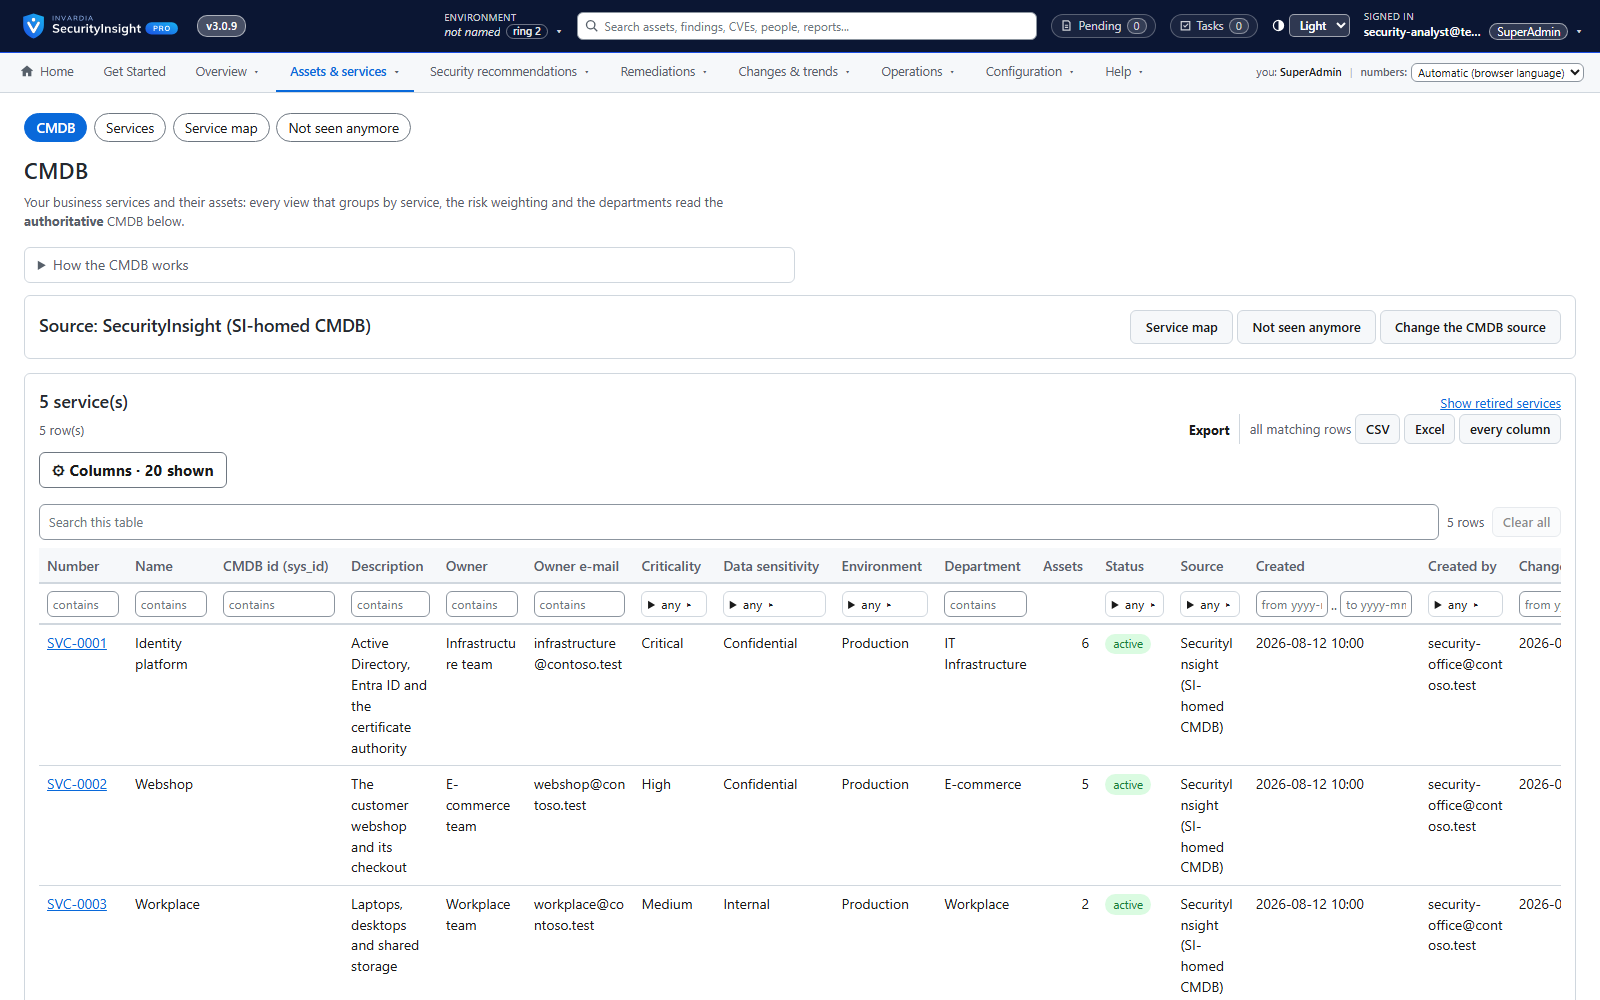
One setting chooses the source of services: SecurityInsight itself, a CSV file, or ServiceNow. In SecurityInsight each service has a number, a name and the familiar CMDB fields (owner, criticality, environment, description), is audited, and is maintained on a CMDB page; a service map in the style of the tier board links assets to services by multi-select and drag. With an external CMDB the map shows the links and edits happen at the source. Only one source is authoritative at a time, and every view, department and risk weight reads services the same way.
Business opportunities
Service-level risk from day one, whether or not you run a CMDB today - and no lock-in when you do.
Related features
Asset profiling across endpoints, identities, Azure and public IPs
One profile per asset - device, identity, Azure resource or public IP - built automatically from the data you already have.
One asset, every source: cross-source correlation
A server seen by Defender, as an Azure VM and in Active Directory becomes one CI with one history.
Privilege tier catalog
Every role and permission in your tenant ranked by what an attacker could do with it - Tier 0 to Tier 3.
Tier board with explained decisions
See every asset in its tier and exactly which signal put it there - and move it with one drag.