

Asset tagging, with a dry run first
Write SecurityInsight's classification back as Defender tags, Azure tags and Entra attributes - after seeing what would change.
Purpose
Other tools and policies can use criticality and ownership only if they are written where those tools look.
Design
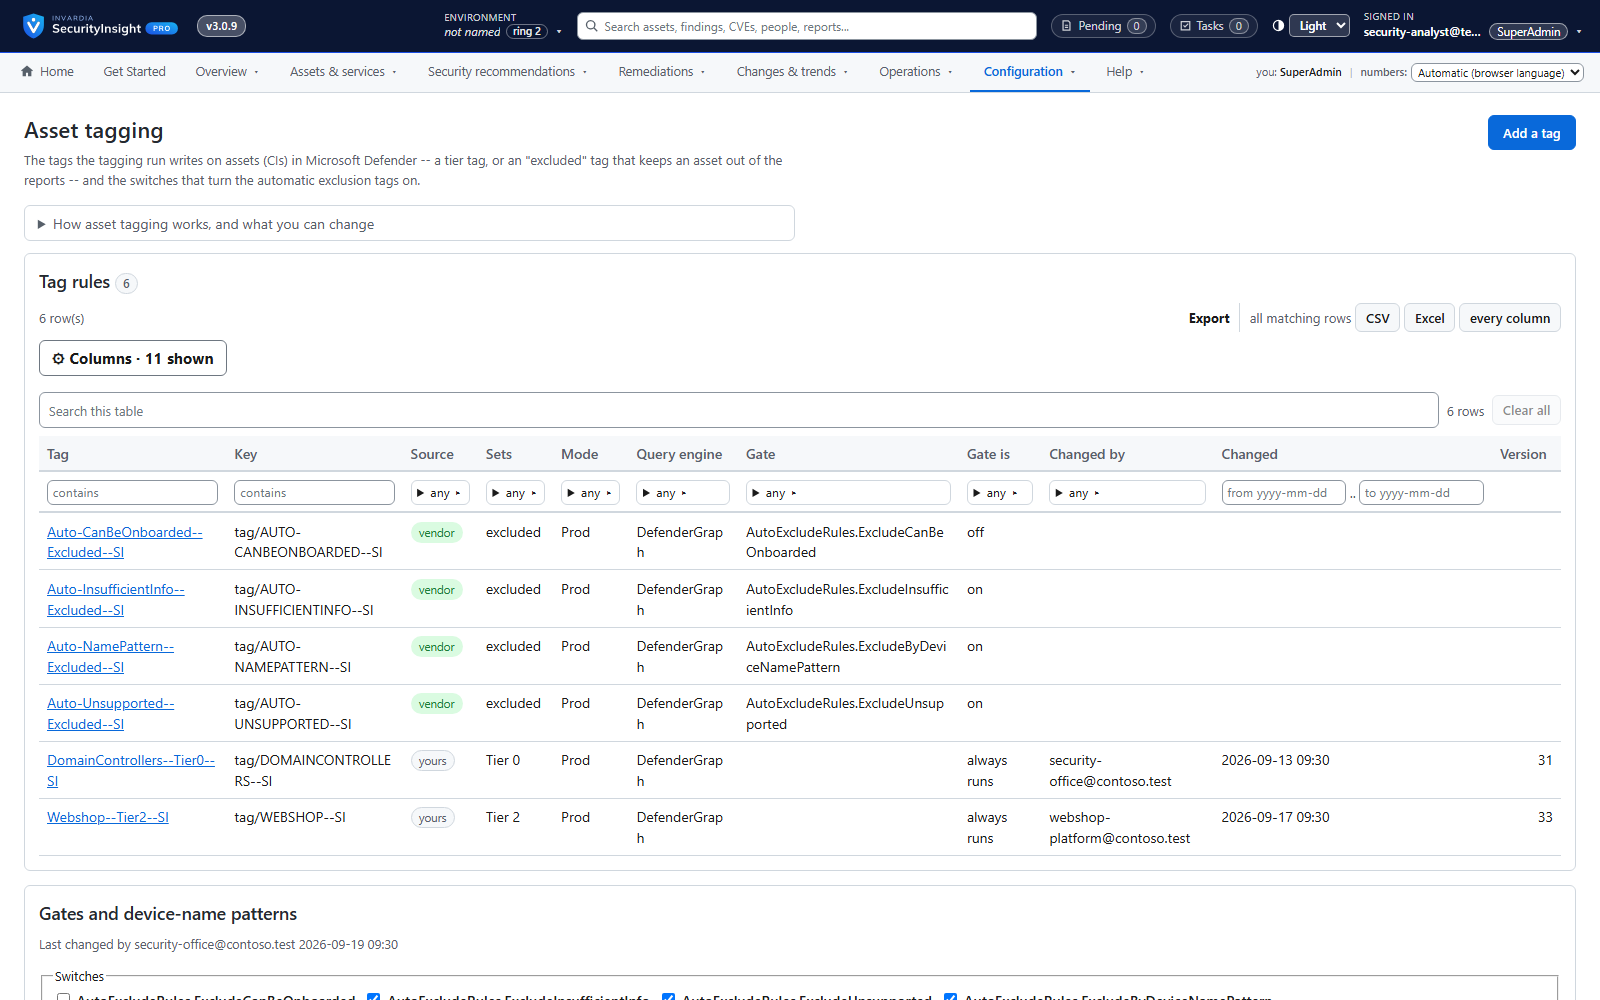
Tagging rules set Defender machine tags, Azure resource tags and Entra custom security attributes. In Community, tagging is a script for a Windows server install: run it with -WhatIfMode to log every tag it would set, then without it to write; the identity it runs as needs the write rights. In Pro, tagging runs as its own container job under its own identity with exactly three write permissions, and stays report-only until a setting turns writing on. Every planned and executed write is logged.
Business opportunities
Put risk context into Defender, Azure Policy and Conditional Access, without giving the collection identity any write rights.
Related features
Asset profiling across endpoints, identities, Azure and public IPs
One profile per asset - device, identity, Azure resource or public IP - built automatically from the data you already have.
One asset, every source: cross-source correlation
A server seen by Defender, as an Azure VM and in Active Directory becomes one CI with one history.
Privilege tier catalog
Every role and permission in your tenant ranked by what an attacker could do with it - Tier 0 to Tier 3.
Tier board with explained decisions
See every asset in its tier and exactly which signal put it there - and move it with one drag.