

MSP: private on both sides, hosted where you choose
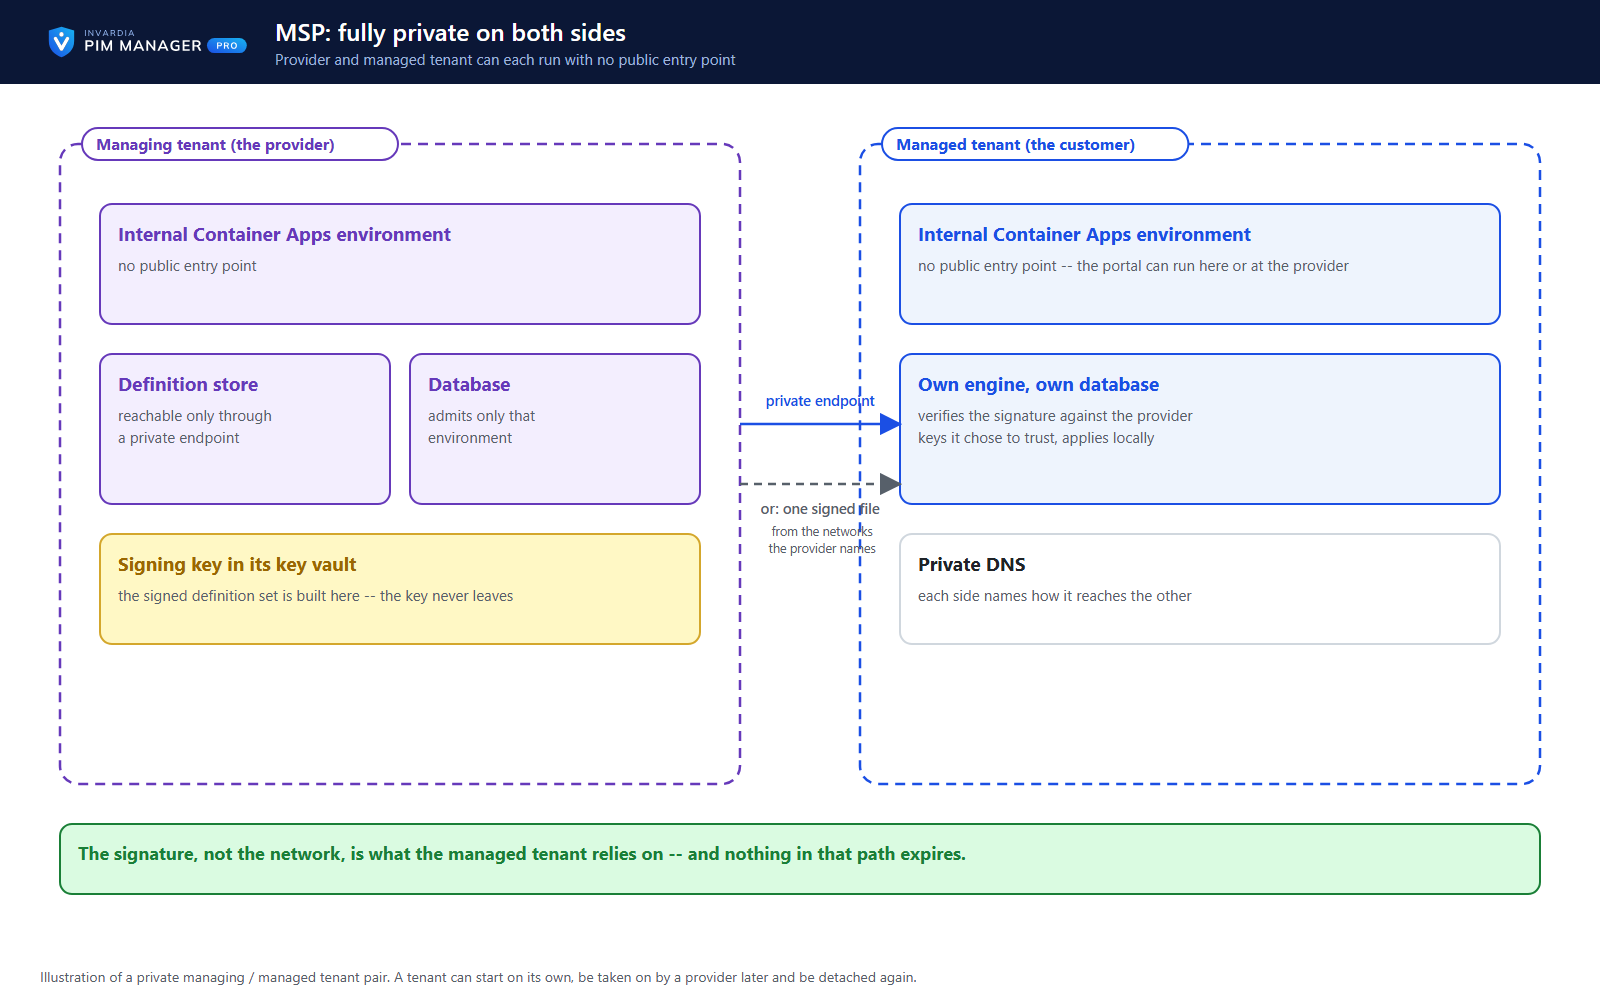
Provider and managed tenant can each run with no public entry point; the managed tenant's Manager can run in the provider's tenant or the customer's own.
Purpose
Regulated customers need the managed service without opening their network to the provider.
Design
Both sides can run in an internal Container Apps environment, with the definition store reachable only through a private endpoint and a database that admits only that environment. Where the networks are not connected, the managed tenant reads the one signed file from the networks the provider names - the signature, not the network, is what it relies on. Each side names how it reaches the other in its own private DNS. A tenant can start on its own, be taken on by a provider later, and be detached again.
Business opportunities
The same managed service fits customers with the strictest network policies - and nobody is locked in.
Related features
PIM policy changes wait for a SuperAdmin
A policy run plans its changes and holds them until a SuperAdmin approves that exact change set, with the setting that weakens protection marked.
Changes only what you define - deleting an account is a person's decision
The engine changes groups, roles and admins only when your data defines them, does not disable, revoke or offboard your break-glass accounts, and does not delete a user account on its own.
Emergency access: break-glass accounts and a time-boxed override
Your break-glass accounts are protected from PIM Manager's revoke, disable and offboard paths, and in an emergency a SuperAdmin can lift the approval requirement for a bounded time.
Scripts and services on the Manager API, on your list only
Scripts and services use the Manager API only with an Entra application that a SuperAdmin lists and a second SuperAdmin approves, as Reader or Admin.