

Vulnerability close-loop: absence is not remediation
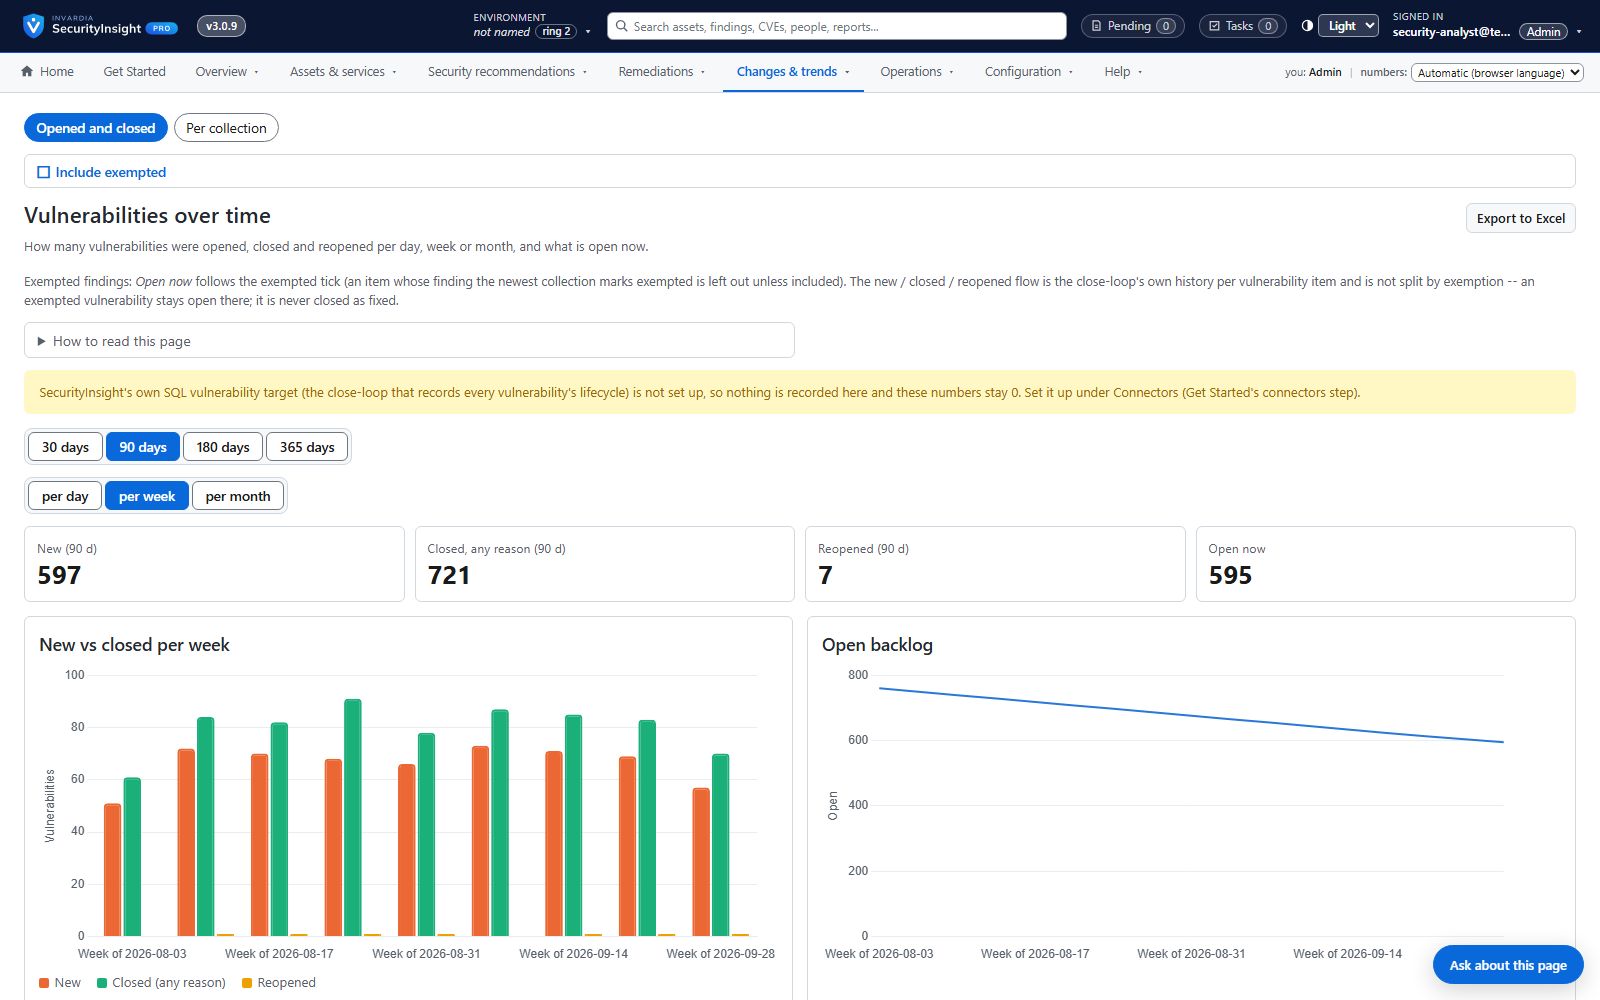
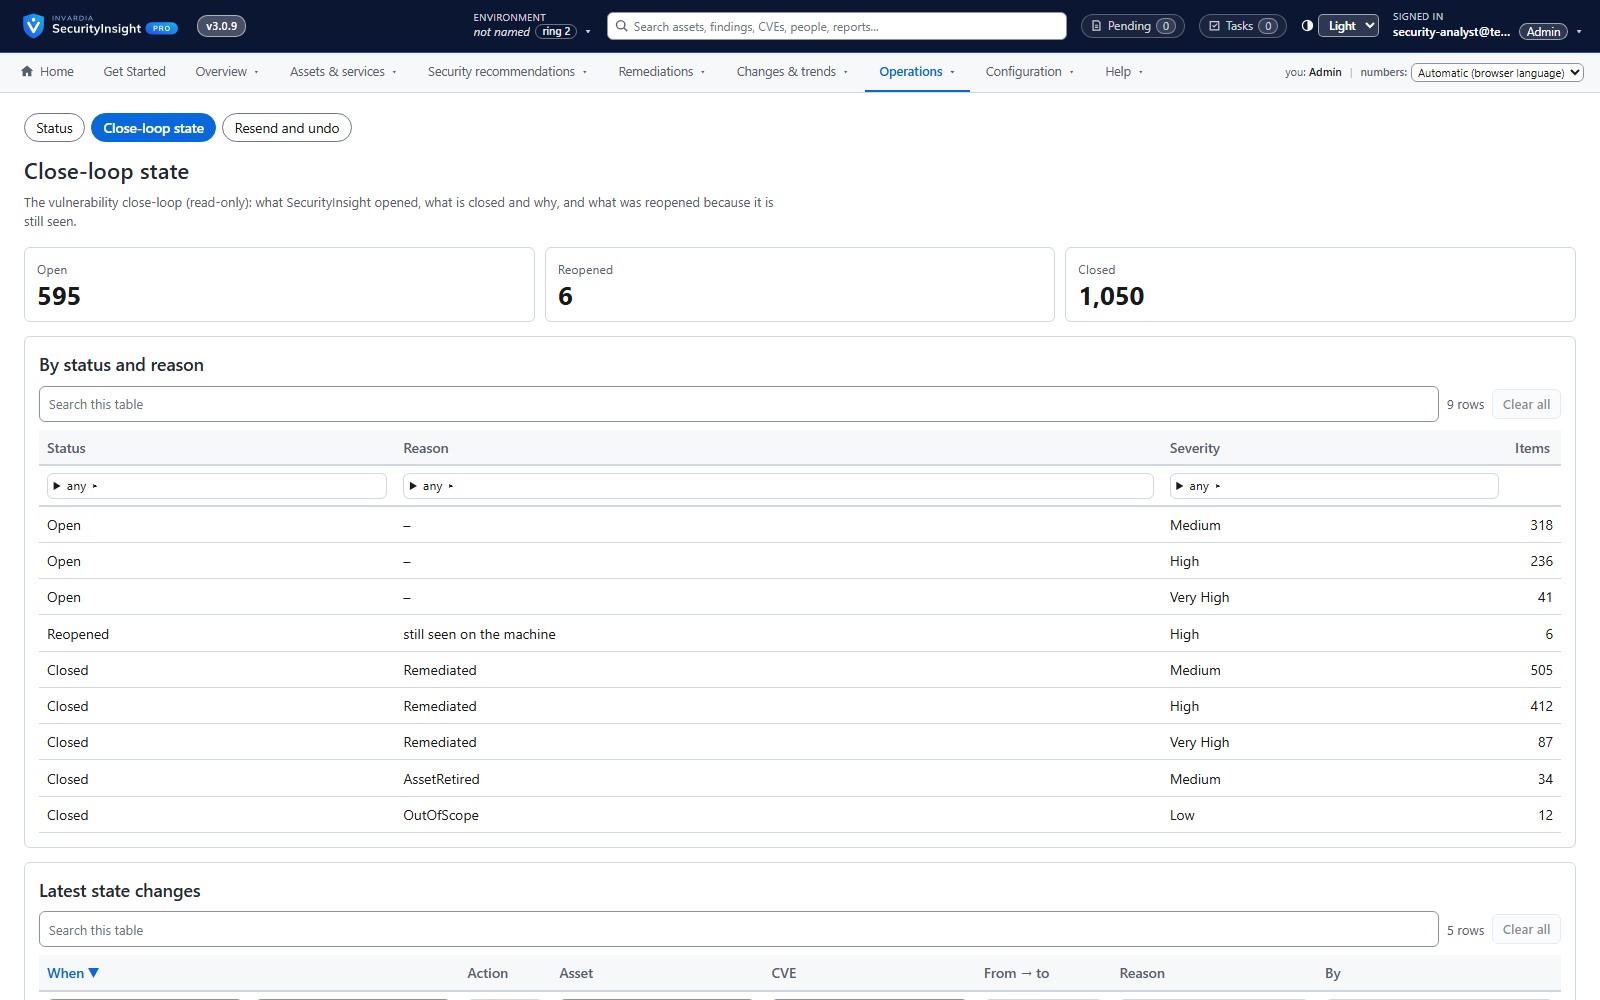
Vulnerabilities are opened, kept current, closed with a reason and reopened if they come back - only on evidence.
Purpose
Ticket systems close vulnerabilities when they disappear from a scan, even when the machine was simply offline - and the next scan reopens them. Metrics become noise.
Design
SecurityInsight tracks every vulnerability on every asset. It closes one as fixed only after several complete runs without it on an asset that was actually seen; a missing asset is unknown and held open, a retired asset closes with that reason, and a fixed one that returns is reopened. A daily mail summarises what opened, closed and reopened, and the time to fix.
Business opportunities
Trustworthy remediation metrics and time-to-fix figures you can put in front of an auditor.
Related features
Asset profiling across endpoints, identities, Azure and public IPs
One profile per asset - device, identity, Azure resource or public IP - built automatically from the data you already have.
Privilege tier catalog
Every role and permission in your tenant ranked by what an attacker could do with it - Tier 0 to Tier 3.
Public IP exposure with Shodan
See your internet-facing addresses the way an attacker does, tied to the asset behind them.
Risk score and weighted risk score
Every finding scored for severity and likelihood, then weighted by the business criticality of its asset.