

Signed updates by ring
Updates arrive ring by ring and are applied only when their signature, version and checksum verify.
Purpose
An update channel is a powerful attack path; customers need to know nothing unverified will ever run.
Design
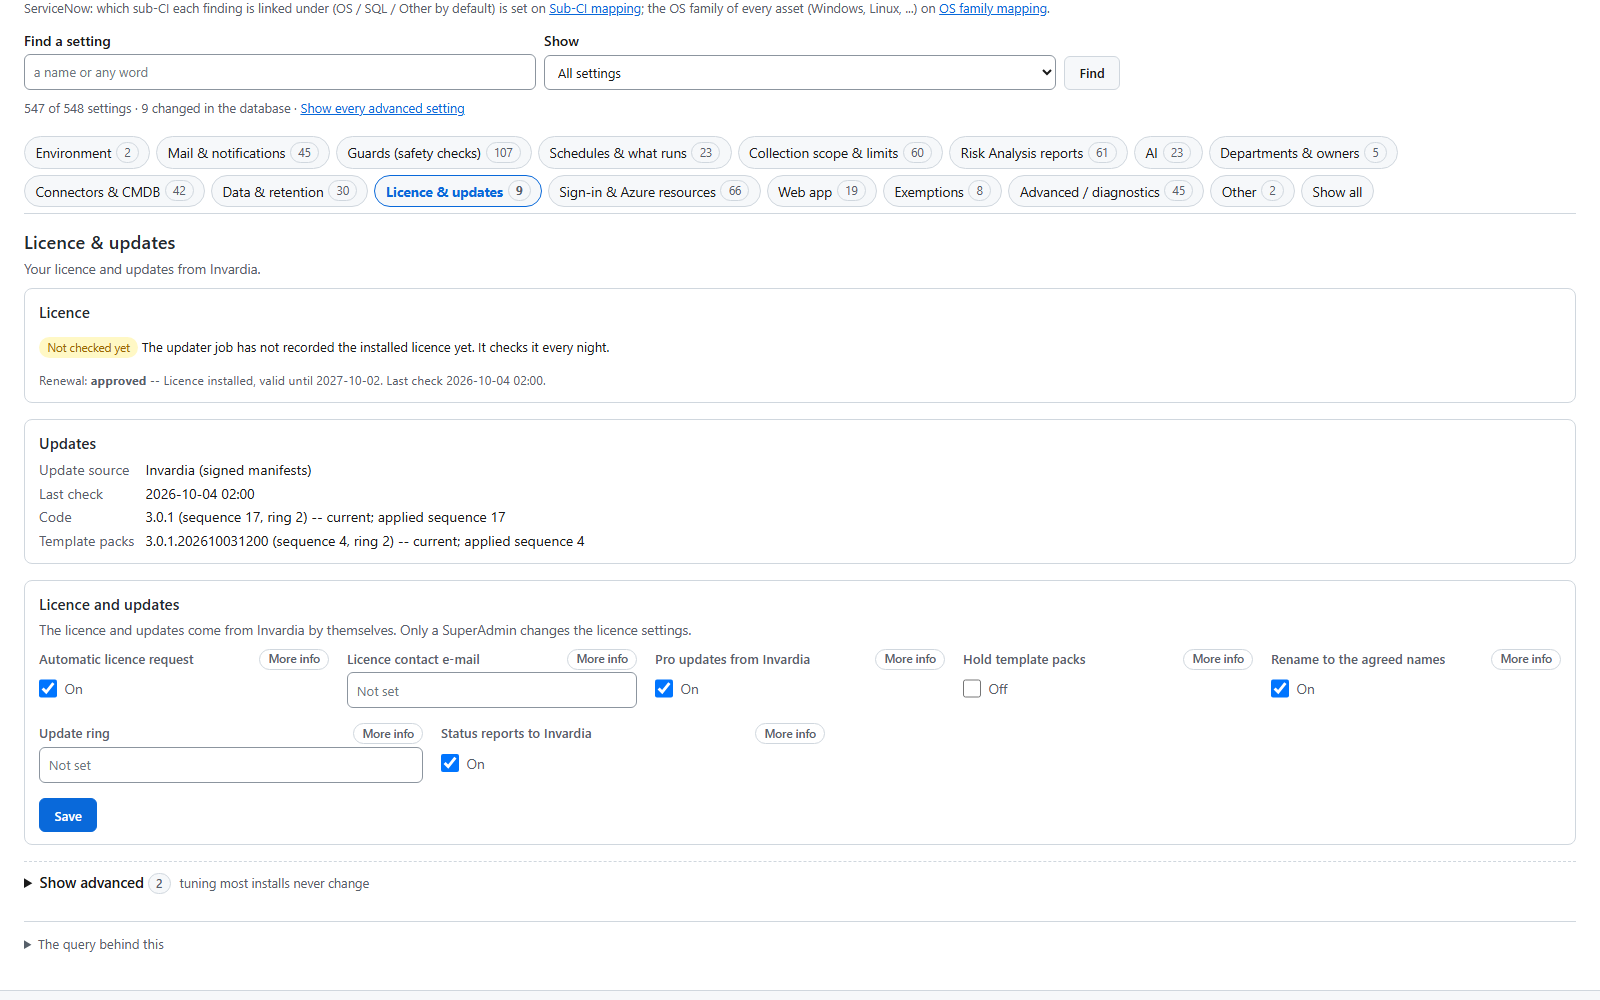
A nightly updater asks Invardia for the release of its update ring with its licence and install key. It applies a release only when the signed manifest verifies against public keys built into SecurityInsight, the product and kind match, the sequence is not older than what is installed, and the download's size and SHA-256 match. A manual step holds the update until you accept it. The updater builds the image in your own registry, rolls the jobs, verifies and rolls back on failure.
Business opportunities
Always current, never surprised - with integrity you can verify.
Related features
Roles and scoped access
Reader, Delegated, Admin and SuperAdmin - checked on the server for every page and every action.
External advisors with a second check
Let trusted consultants review and recommend for a department - and approve only after a second check.
Template releases by update ring, with roll back
New detection rules and reports arrive by ring, are reviewed per detection method, and can be rolled back.
Asset tagging, with a dry run first
Write SecurityInsight's classification back as Defender tags, Azure tags and Entra attributes - after seeing what would change.