

Roles and scoped access
Reader, Delegated, Admin and SuperAdmin - checked on the server for every page and every action.
Purpose
Not everyone should change everything. Teams need to act on their own area without holding the keys to the whole install.
Design
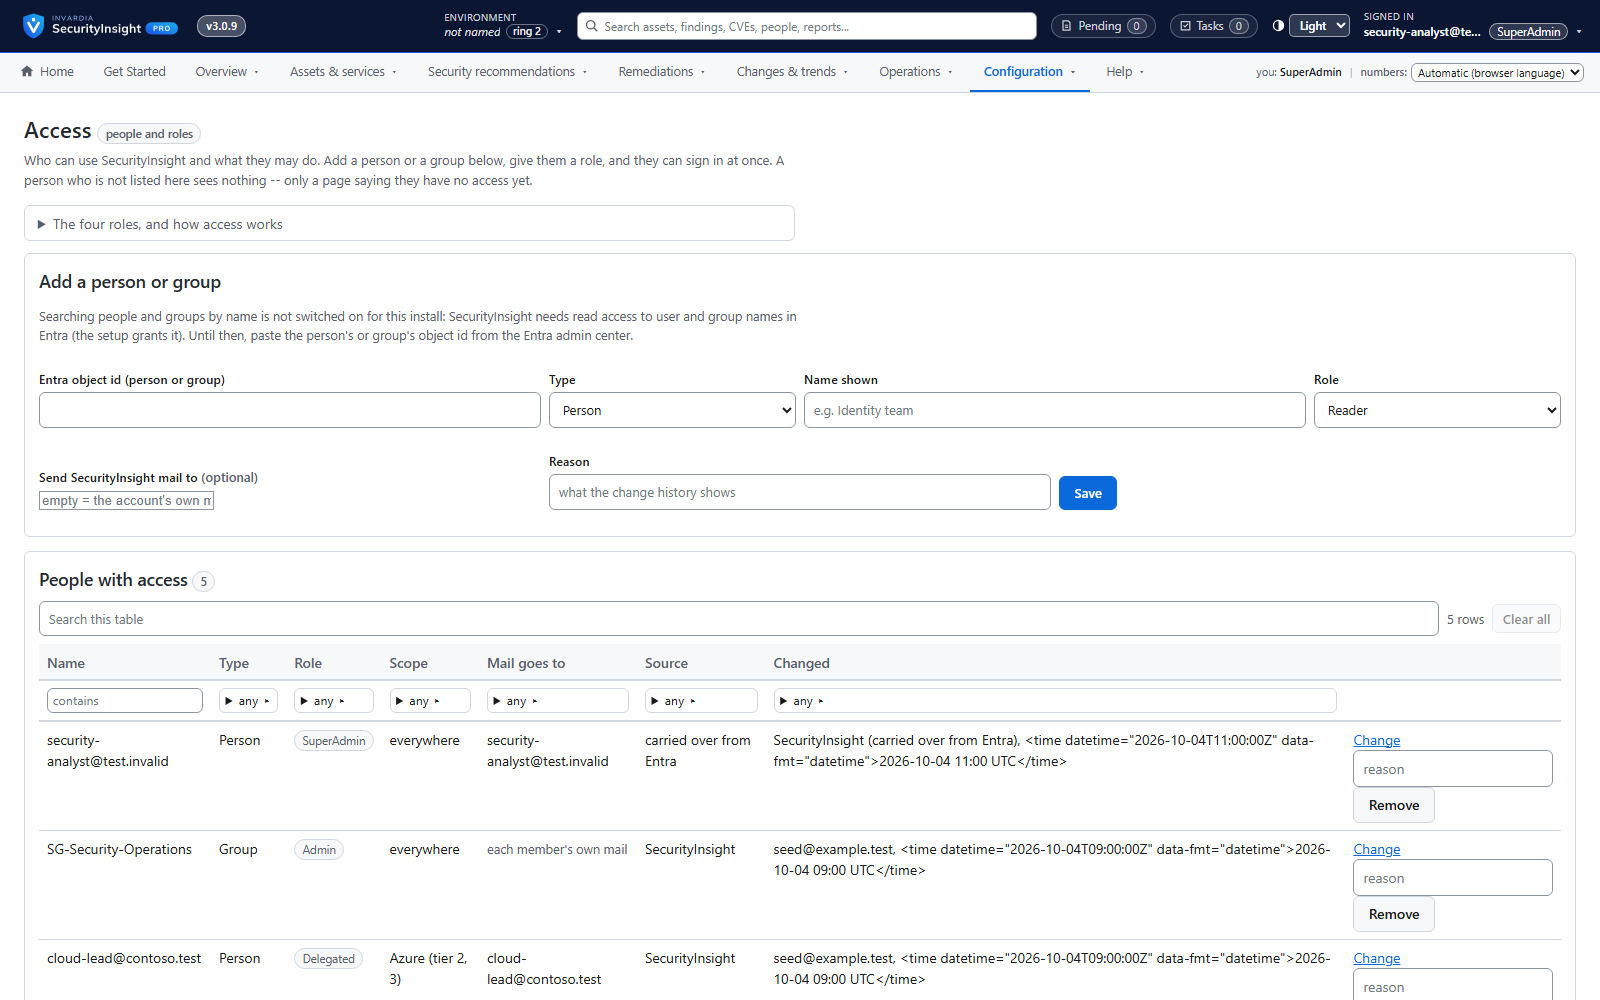
Entra app roles decide who can sign in. On top, a SuperAdmin maps Entra users and groups to a role: Reader sees and exports, Delegated changes only inside the scopes assigned (security domain, optionally asset kinds and tiers), Admin manages the install, SuperAdmin also manages roles, the licence, updates and template releases. A bulk action outside the scope is refused as a whole, and every access change is in the change history.
Business opportunities
Safe delegation to domain teams and a clear separation of duties for audits.
Related features
Tier board with explained decisions
See every asset in its tier and exactly which signal put it there - and move it with one drag.
Business services ranked by weighted risk
See which business services carry the most risk, and drill down to the assets and findings behind them.
A CMDB in SecurityInsight - or your own
Keep your service catalog in SecurityInsight, or connect the CMDB you already have.
Connectors: ServiceNow, SQL and any REST system
Send vulnerabilities to ServiceNow, a SQL table or any risk or ticketing system - safely.