

Connectors: ServiceNow, SQL and any REST system
Send vulnerabilities to ServiceNow, a SQL table or any risk or ticketing system - safely.
Purpose
Findings only reduce risk when they reach the people and systems that do the work.
Design
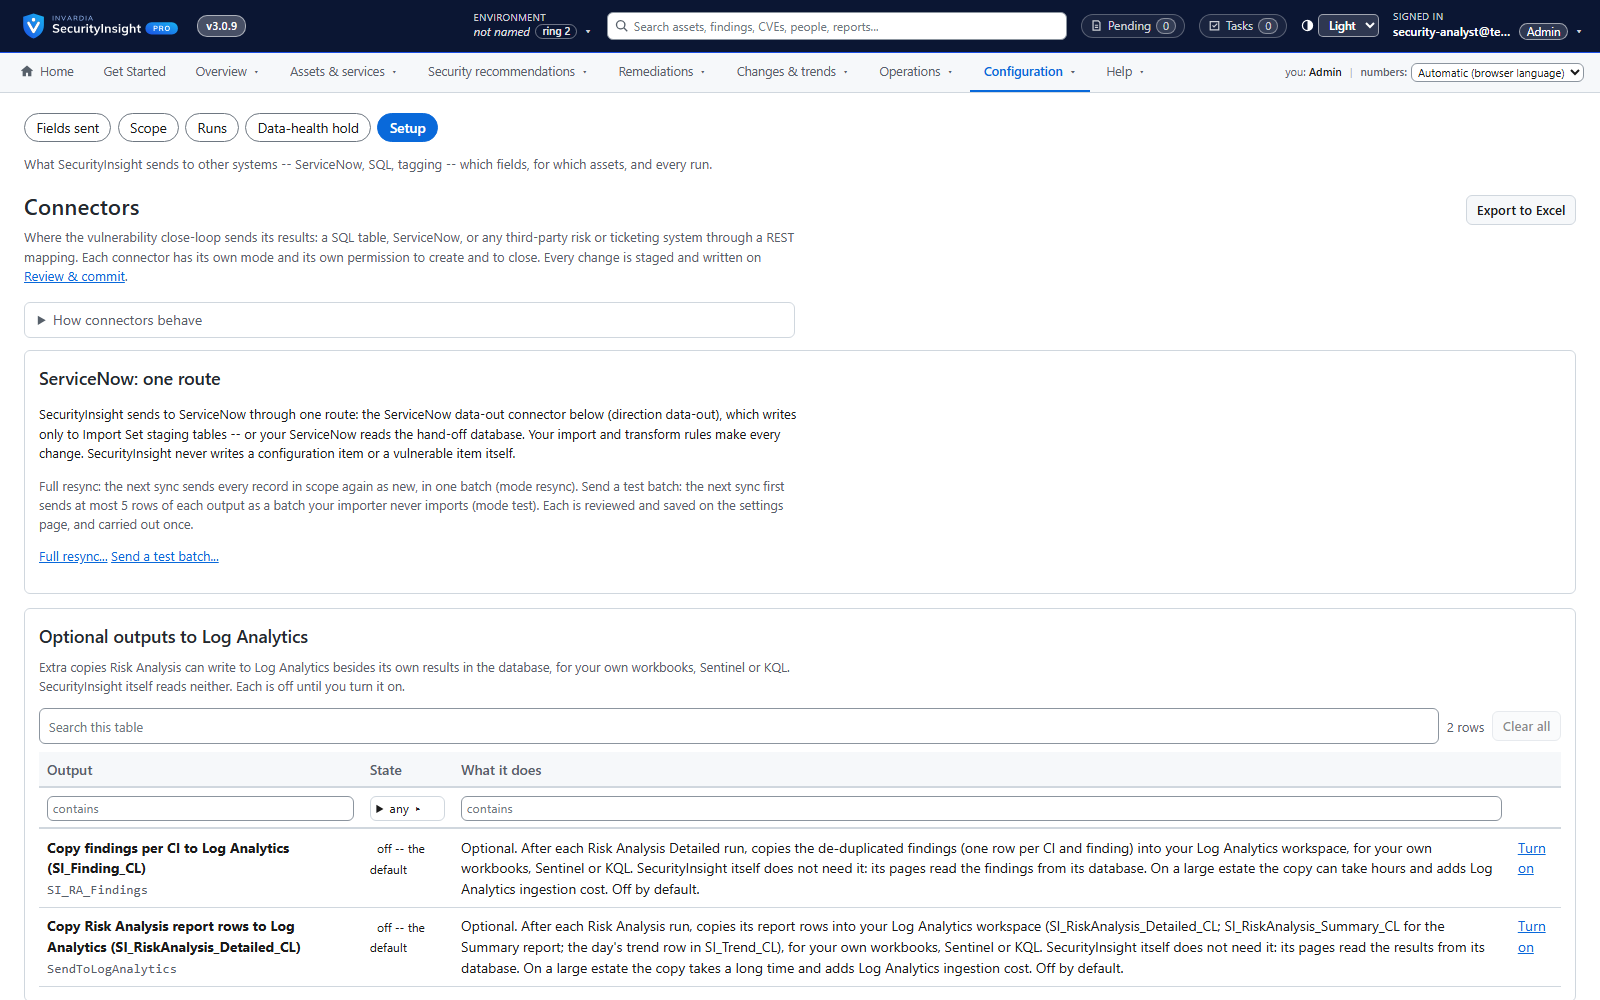
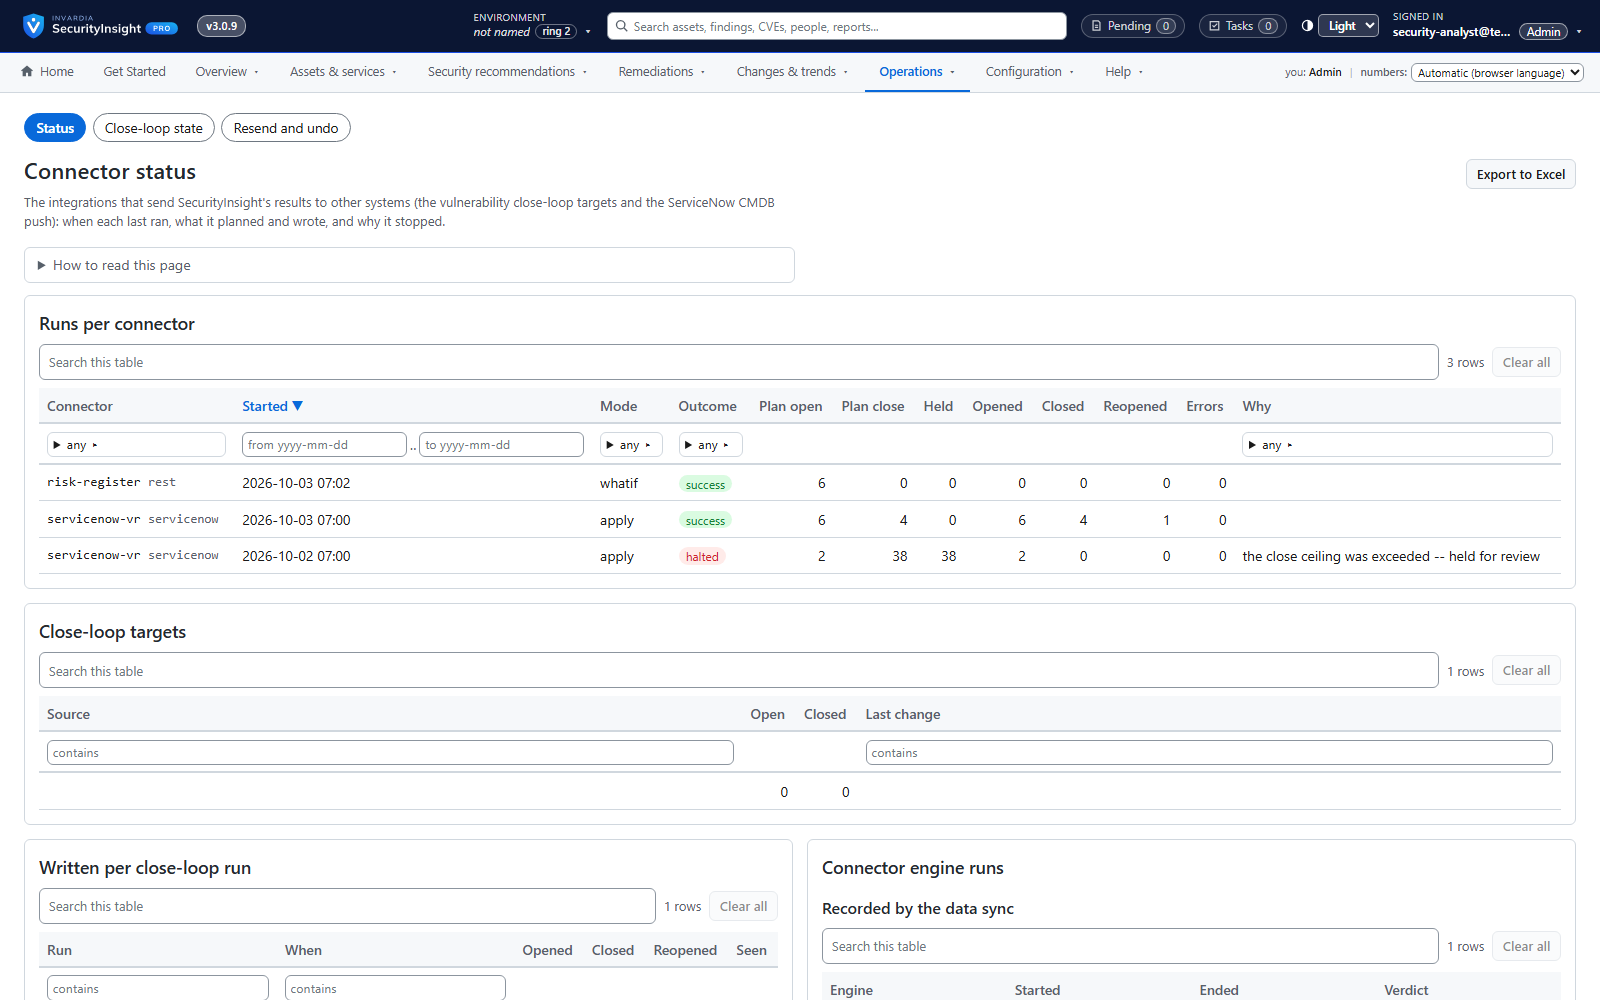
Each connector has its own mode - plan first, then apply - and its own permission to create and to close. A REST connector is described by a mapping, so a new system needs no code. Connectors change only the items they created, every close follows the close-loop rule, and a large or sudden drop is held for a person to review. Credentials stay in your Key Vault; the connector stores only their names. A ServiceNow CMDB feed matches and creates configuration items.
Business opportunities
Automated, auditable hand-over to the teams that fix things, without risking a flood of wrong tickets.
Related features
Tier board with explained decisions
See every asset in its tier and exactly which signal put it there - and move it with one drag.
Risk Analysis reports: Excel, mail and AI summary
138 ready-made reports across identity, endpoint, Azure and public IP - delivered as a workbook, a mail and an optional AI summary.
Findings workspace with Excel export
Every finding of a collection, most important first - filter, pivot, drill down and export to Excel.
Fifteen views of every collection
Raw rows, correlated CIs, vulnerabilities, risk, MITRE, compliance, CVSS, exemptions, lifecycle, what changed, connector changes and services - for any collection.