

MITRE ATT&CK and compliance views
See which attack stages your findings leave open and which compliance controls they touch.
Purpose
Auditors and boards ask about frameworks and attack techniques, not about individual CVEs.
Design
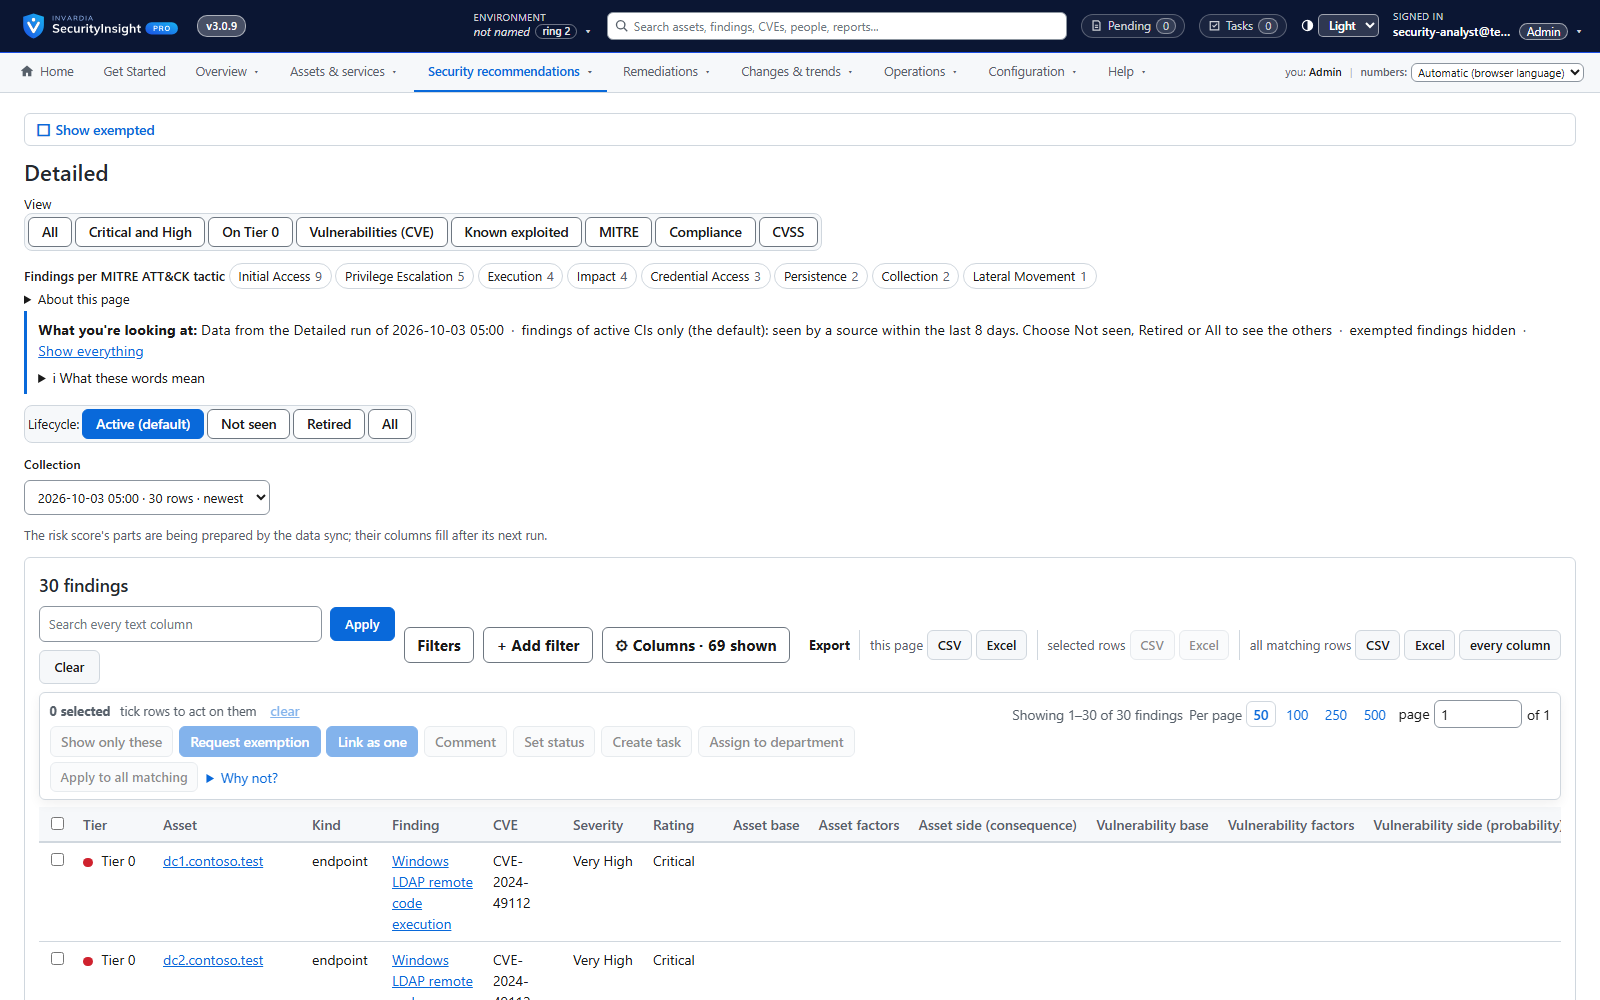
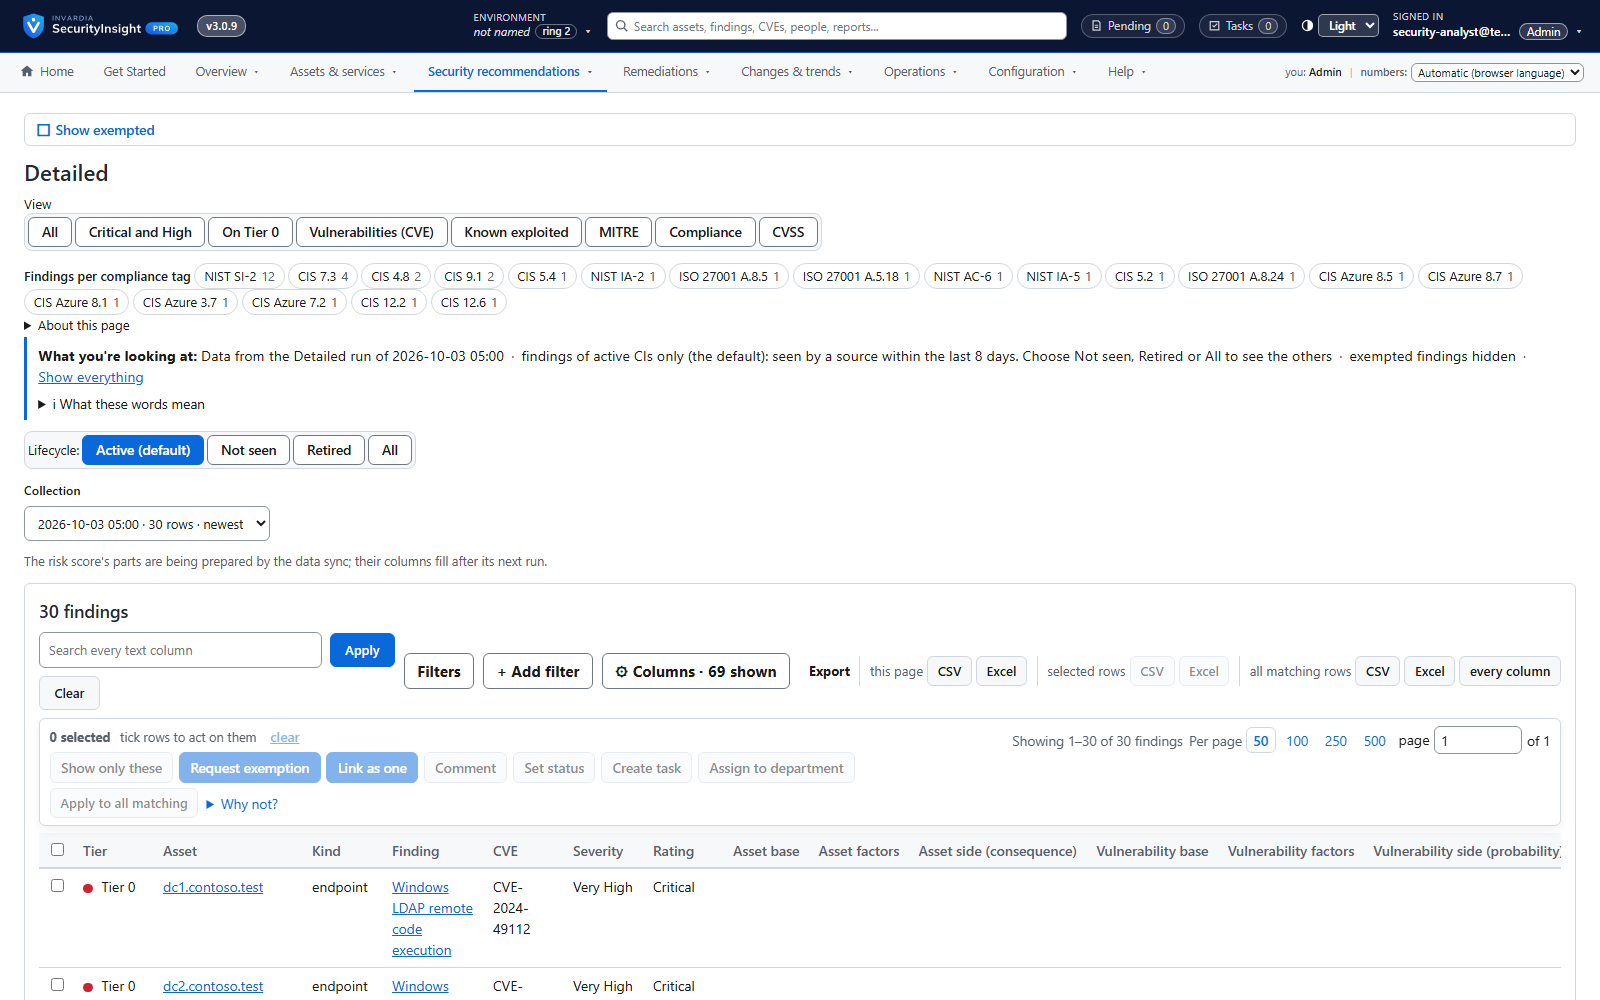
Findings carry their MITRE ATT&CK tactics and techniques and compliance tags. The MITRE view counts findings, CIs and risk per tactic and technique; the compliance view does the same per compliance tag; both filter straight down to the findings behind each number.
Business opportunities
Evidence for NIS2, DORA, ISO 27001 or CIS conversations in the language auditors use, straight from operational data.
Related features
Risk Analysis reports: Excel, mail and AI summary
138 ready-made reports across identity, endpoint, Azure and public IP - delivered as a workbook, a mail and an optional AI summary.
Risk trends over time
Is the estate getting safer? Daily trends by tier, severity, domain or report.
Management views and Tier-0 focus
Top risks, risk by domain, new versus fixed and Tier-0 exposure on one menu.
Vulnerability close-loop: absence is not remediation
Vulnerabilities are opened, kept current, closed with a reason and reopened if they come back - only on evidence.