

Governed exemptions
Accepted risk is requested, approved per security domain, time-limited and reviewed every month.
Purpose
Exemptions that live in a spreadsheet or a comment never expire, have no owner and cannot be shown to an auditor.
Design
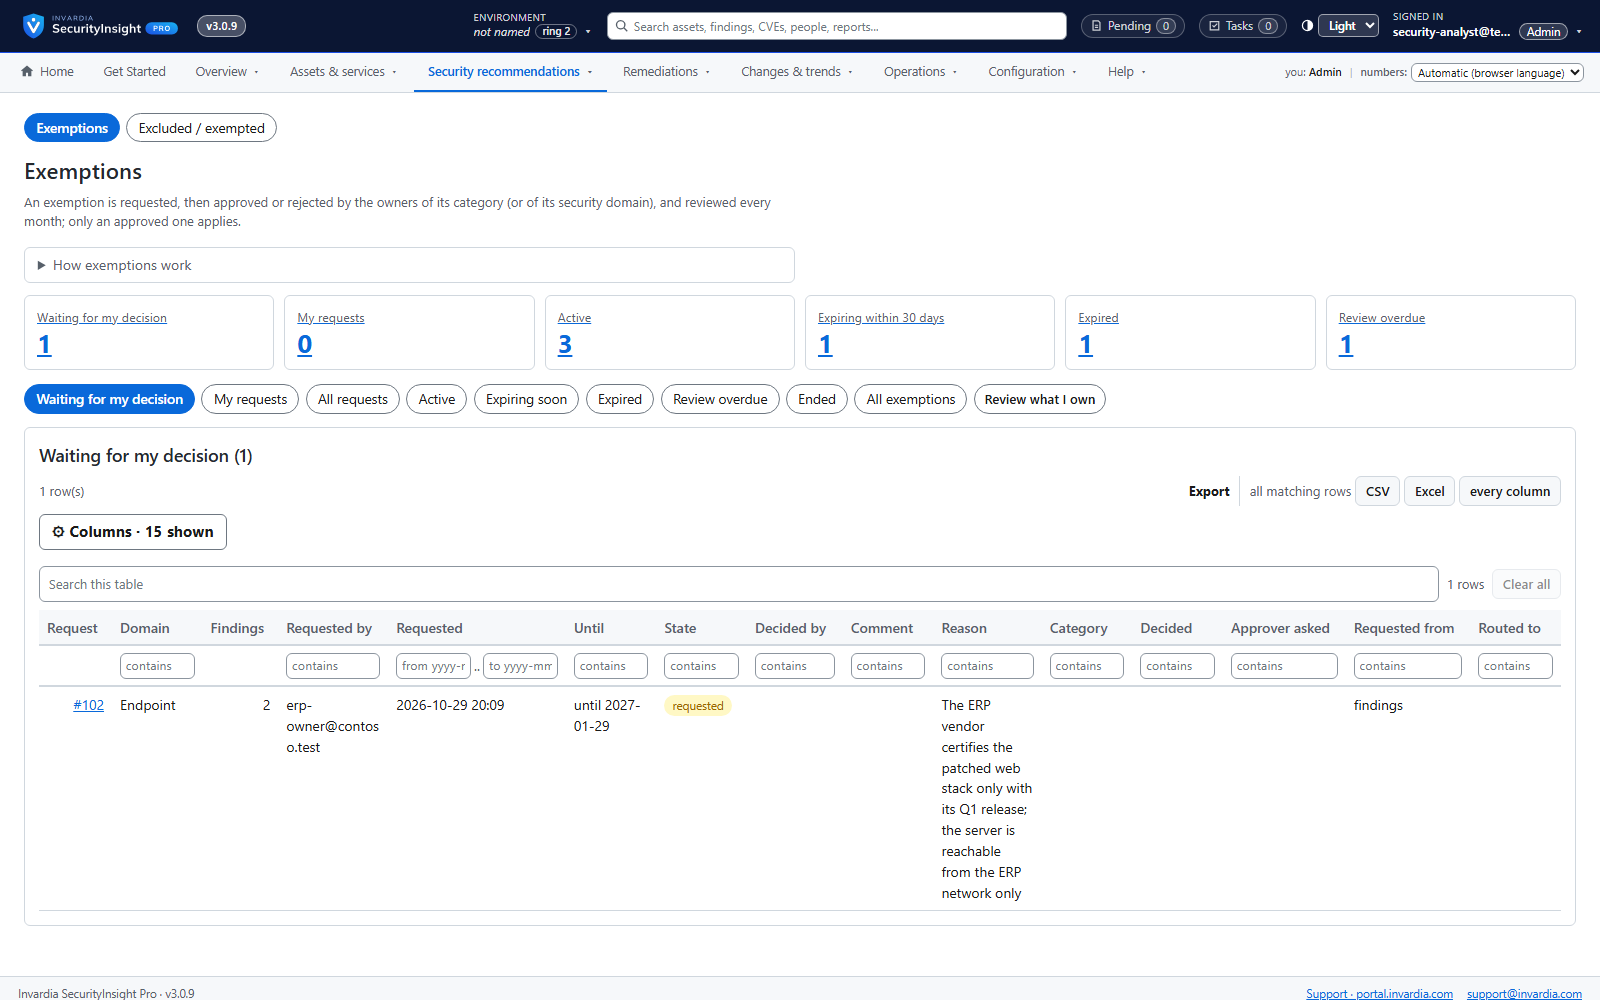
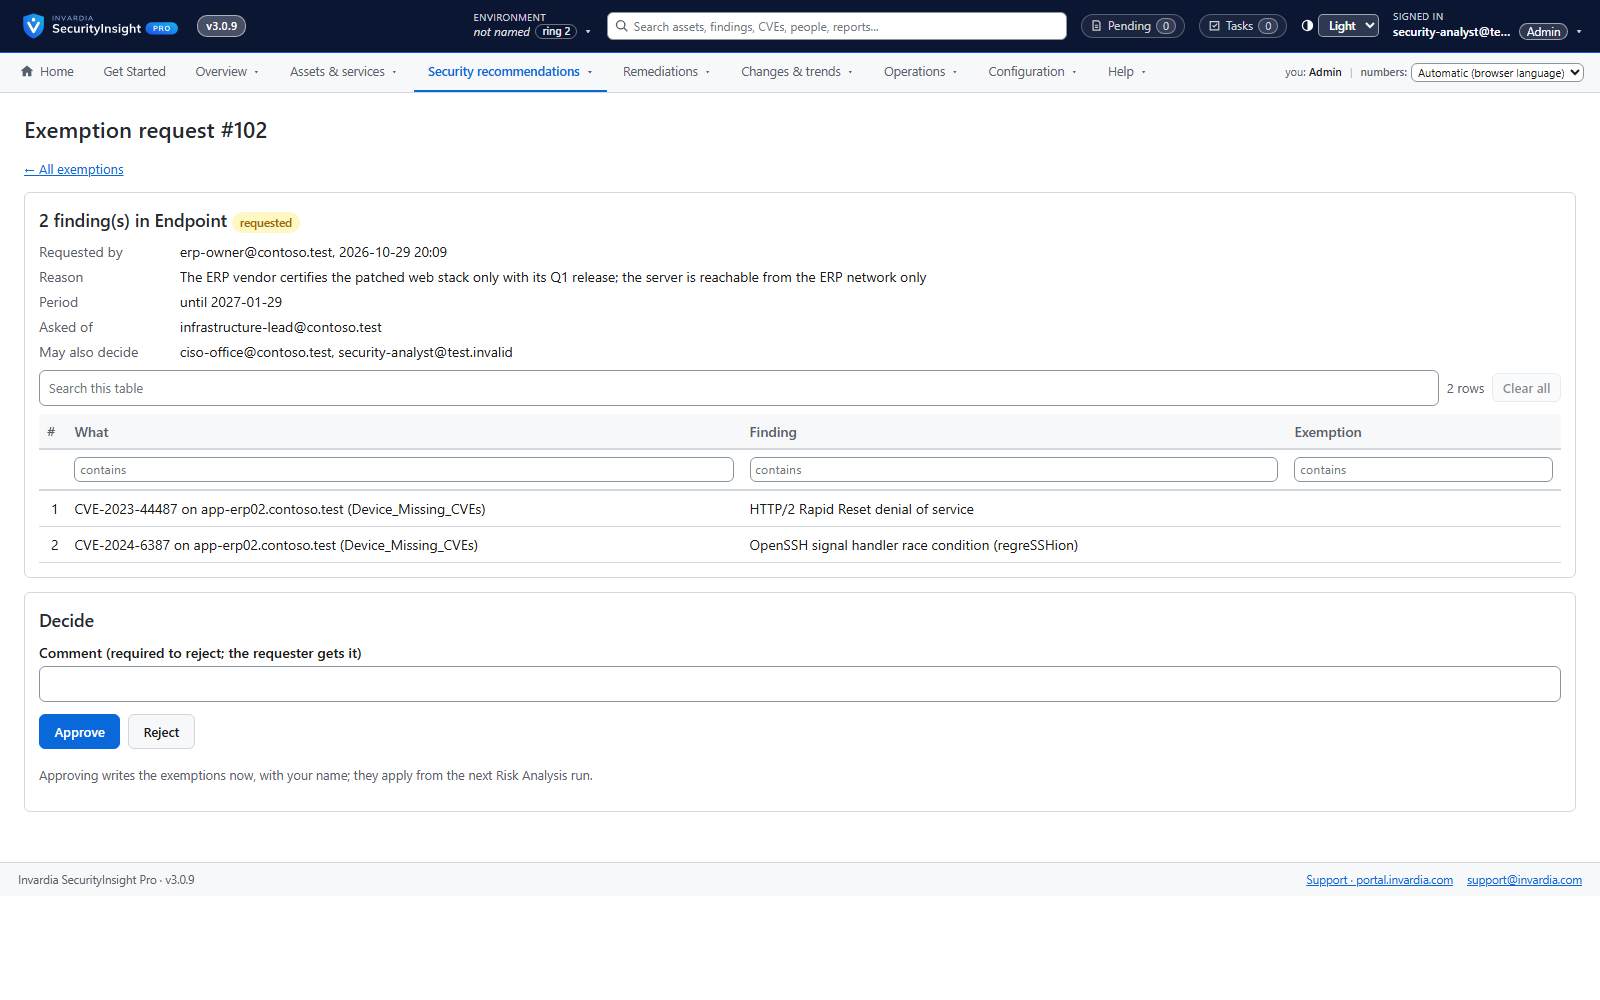
Owners and approvers are named per security domain. Anyone with access requests an exemption for selected findings or everything matching a filter, with a reason and a period of 3, 6 or 12 months or a date. An approver approves or rejects with a comment; only approved exemptions apply. Owners get a monthly review mail and extend, keep or end each exemption; expiry warnings and overdue reviews are flagged. Every step is in the change history.
Business opportunities
Accepted risk with a name, a reason and an end date - exactly what auditors and regulators expect.
Related features
Tier board with explained decisions
See every asset in its tier and exactly which signal put it there - and move it with one drag.
Risk Analysis reports: Excel, mail and AI summary
138 ready-made reports across identity, endpoint, Azure and public IP - delivered as a workbook, a mail and an optional AI summary.
MITRE ATT&CK and compliance views
See which attack stages your findings leave open and which compliance controls they touch.
Risk trends over time
Is the estate getting safer? Daily trends by tier, severity, domain or report.