

Departments own assets and recommendations
Every asset and recommendation has a department, its owners see their own work, and nothing falls between chairs.
Purpose
Security cannot fix everything itself. Responsibility for an asset or a recommendation must sit with the department that runs it.
Design
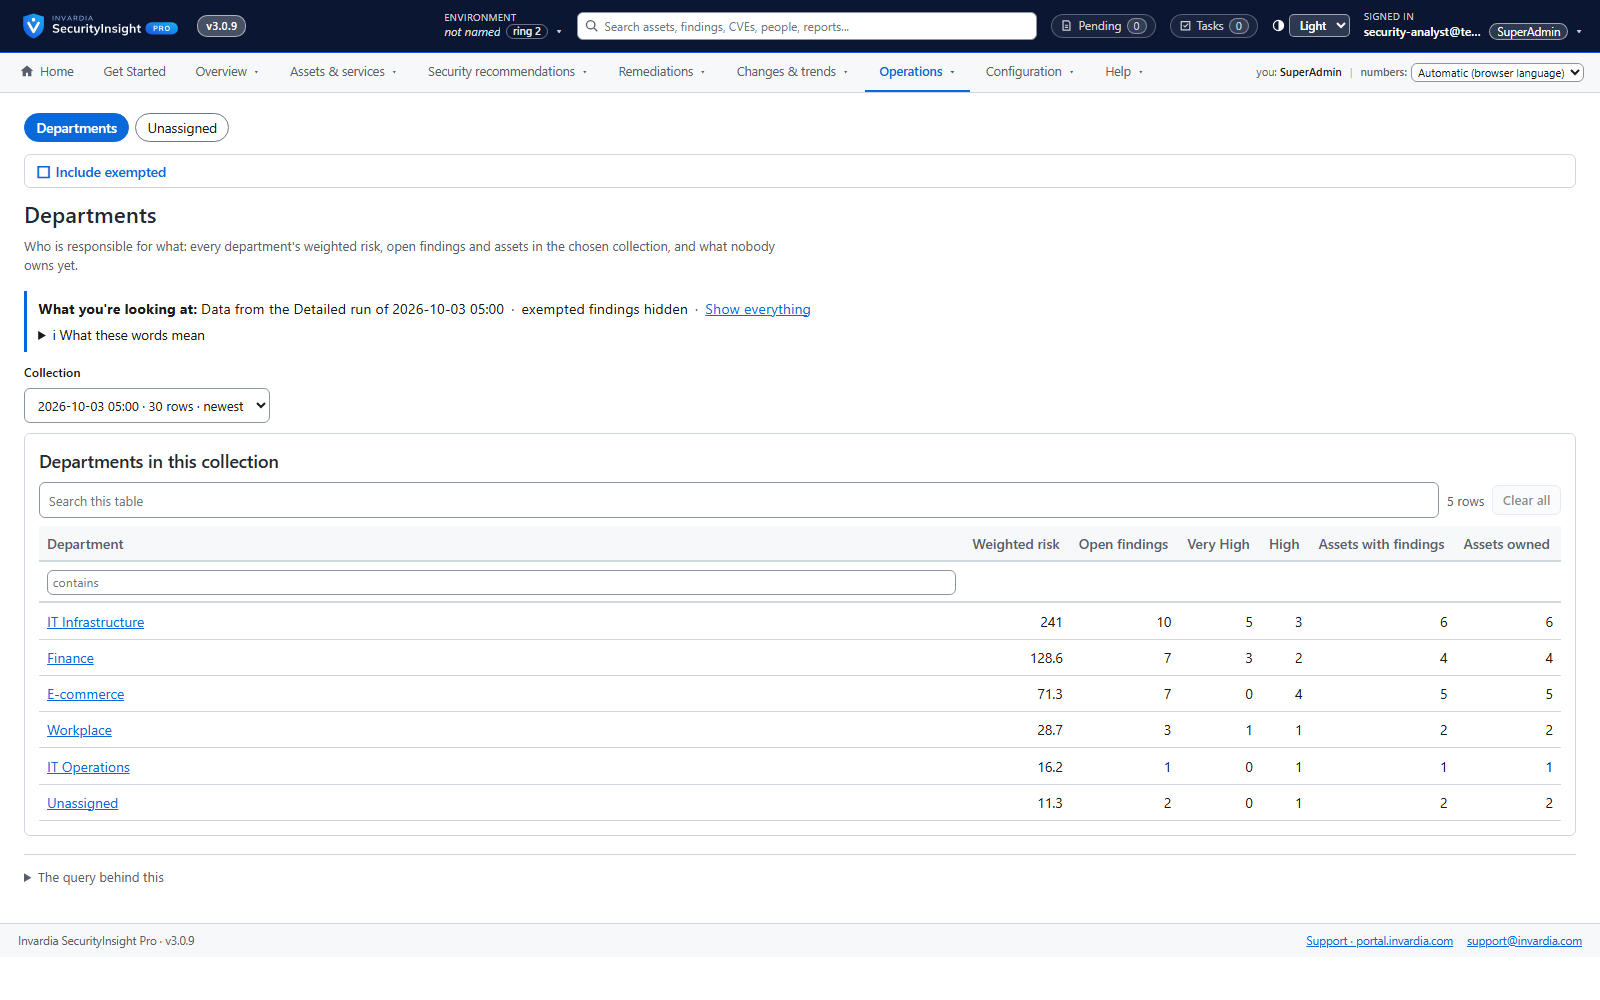
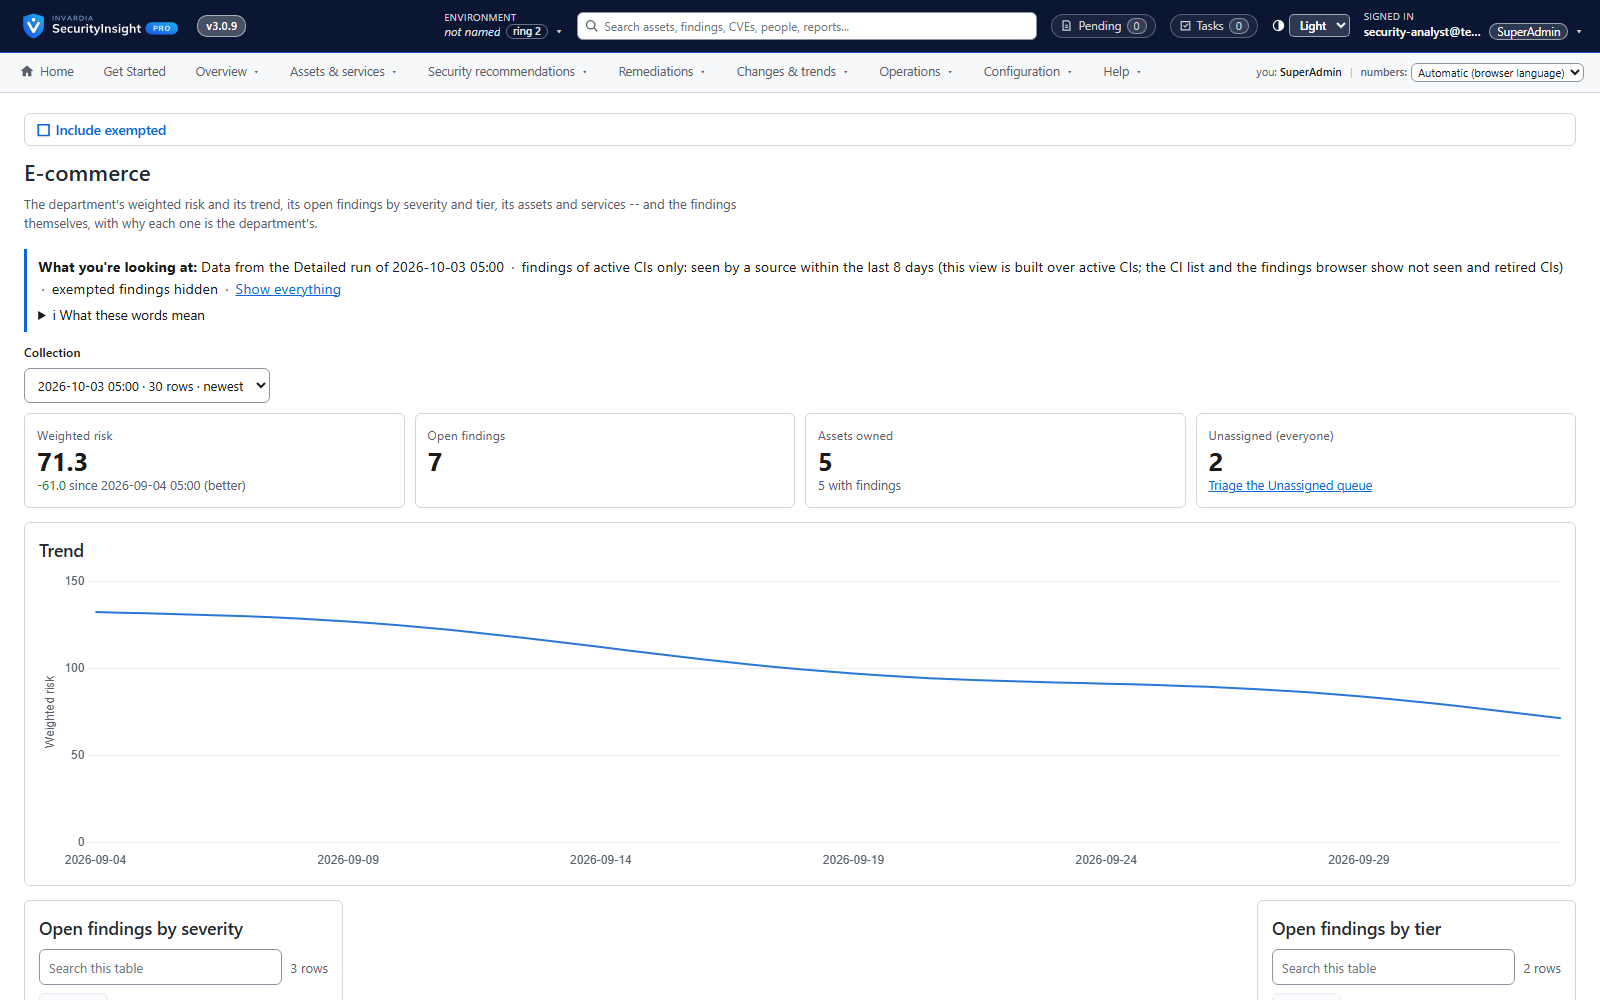
Departments have technical and business owners, approvers and delegates. An asset's department comes from a policy - platform tags first, then SecurityInsight rules - or from an override per asset or per recommendation; the recommendation override wins over the asset override, which wins over the policy, and anything left lands in an Unassigned queue. Department members are Delegated users who see only the assets and findings they are responsible for, with a per-department overview, a governance log of comments per finding, notifications, a monthly review and remediation flows per category.
Business opportunities
Clear accountability across the organisation and less chasing by the security team.
Related features
Tier board with explained decisions
See every asset in its tier and exactly which signal put it there - and move it with one drag.
Business services ranked by weighted risk
See which business services carry the most risk, and drill down to the assets and findings behind them.
A CMDB in SecurityInsight - or your own
Keep your service catalog in SecurityInsight, or connect the CMDB you already have.
Connectors: ServiceNow, SQL and any REST system
Send vulnerabilities to ServiceNow, a SQL table or any risk or ticketing system - safely.