

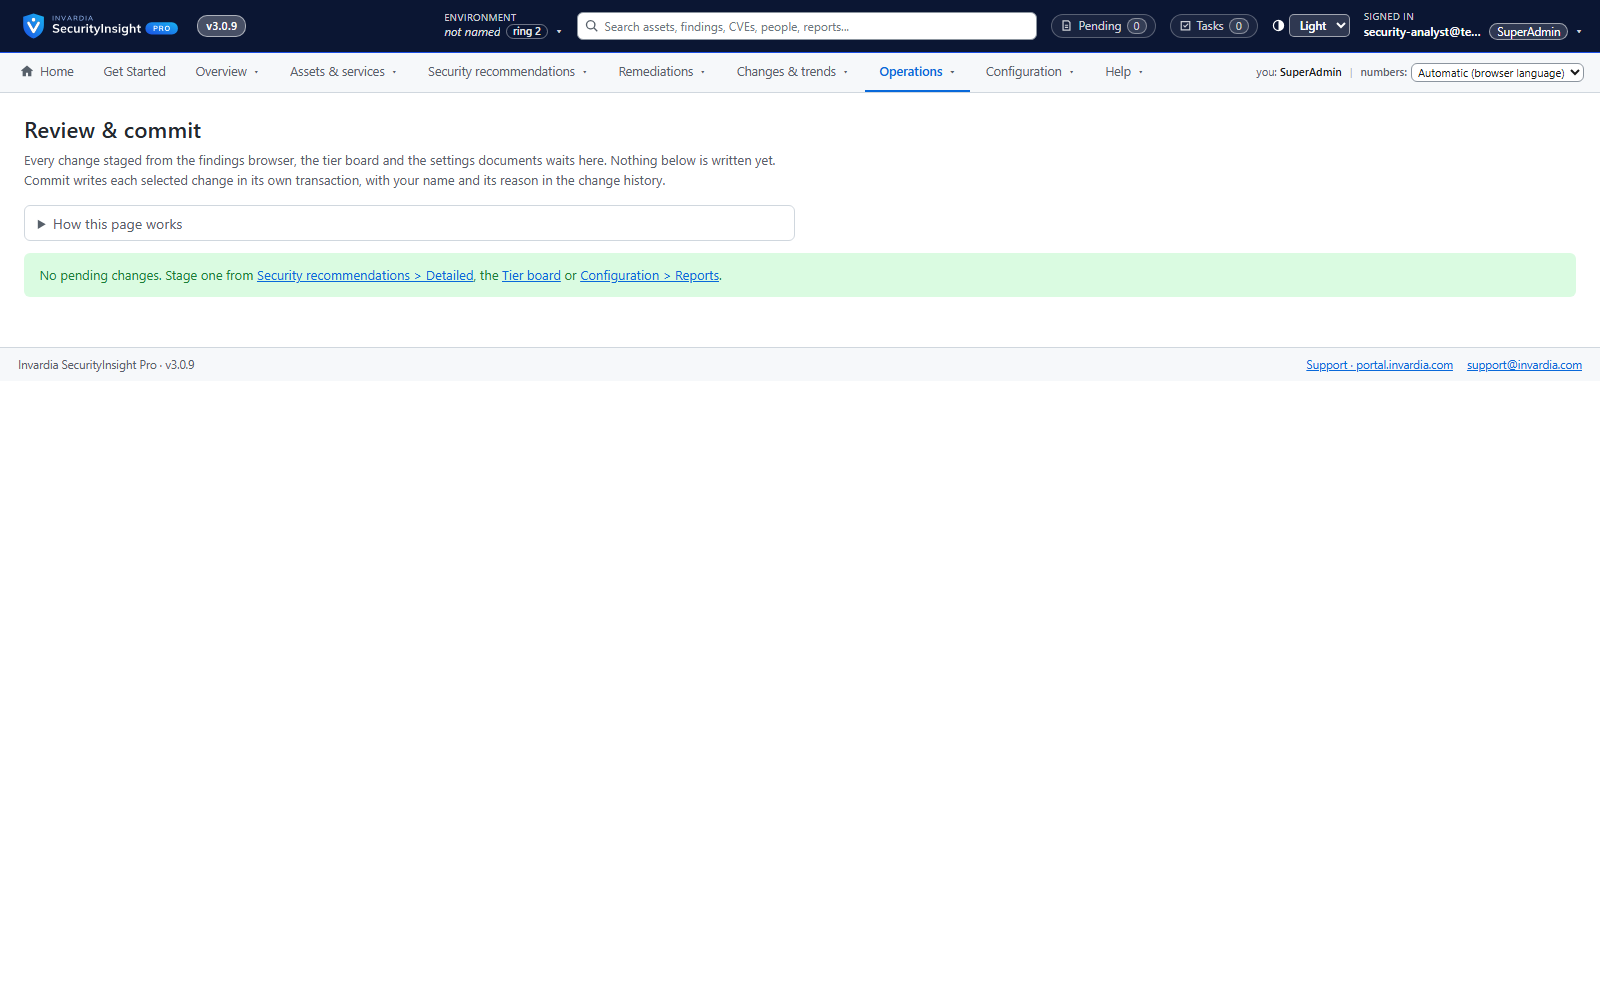
Review & commit and full change history
Nothing is written directly: changes are staged, reviewed and committed with a reason and an audit row.
Purpose
Unreviewed changes to tiers, rules and settings are a risk of their own, and auditors want to know who changed what.
Design
Tier moves, exclusions, weights, rules and settings are staged with a reason and written only on Review & commit, each in one transaction with an audit row; access is re-checked at commit. Nothing is deleted. The change history lists every change with who, when, old and new value and why.
Business opportunities
Four-eyes control and a complete audit trail without slowing the team down.
Related features
Tier board with explained decisions
See every asset in its tier and exactly which signal put it there - and move it with one drag.
Risk Analysis reports: Excel, mail and AI summary
138 ready-made reports across identity, endpoint, Azure and public IP - delivered as a workbook, a mail and an optional AI summary.
MITRE ATT&CK and compliance views
See which attack stages your findings leave open and which compliance controls they touch.
Risk trends over time
Is the estate getting safer? Daily trends by tier, severity, domain or report.